General
What Is a Checksum? How File Verification Really Works

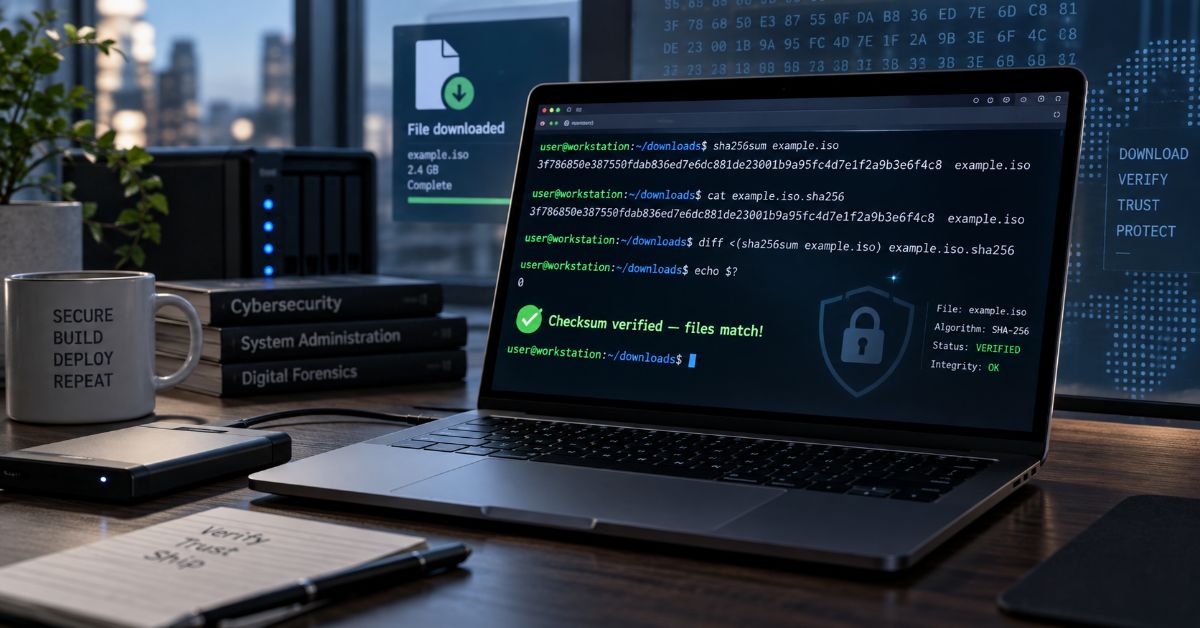
A checksum is a compact value calculated from a file or block of data so you can detect whether the underlying bytes changed – and that simple comparison can stop a corrupted or substituted download before you run it. If you searched what is a checksum, the practical answer is this: calculate the value from the file you received, use the same algorithm as the publisher, and compare the complete result with a trusted reference.
The important word is trusted. Many explanations treat a matching checksum as proof that a file is safe or authentic. It is not. A match tells you that your copy corresponds to the reference digest you used. If the reference came from the same compromised server as a malicious file, an attacker could potentially replace both. That distinction between integrity and authenticity is the part I think matters most in real use.
Checksums appear everywhere: operating-system images, software packages, backups, archive workflows, network protocols, storage systems, and digital-preservation programs. The algorithms behind them range from fast error-detection codes such as CRC to cryptographic hash functions such as SHA-256 and SHA-512. Those tools solve related problems, but they do not offer the same resistance to intentional manipulation.
In this guide, I will show how checksum verification actually works, how a checksum differs from a hash or digital signature, which algorithms still make sense in 2026, and the built-in commands I would use on Windows, macOS, and Linux. I will also cover mismatch troubleshooting and the trust-chain problem that most short definitions leave out. The goal is not just to recognize a long hexadecimal string. It is to know what conclusion you can safely draw from it.
What Is a Checksum, Exactly?
A checksum is a derived value calculated from input data and later recomputed to detect change. The checksum is much smaller than the original file. For a cryptographic hash, the output length is fixed for the algorithm: SHA-256, for example, produces a 256-bit digest regardless of whether the input is a one-line text file or a multi-gigabyte disk image.
The comparison works because the same input processed by the same deterministic algorithm produces the same result. Change the input bytes and the result normally changes. That gives you a compact way to compare file states without manually examining every byte.
How does checksum verification work?
- The publisher or system calculates a checksum from the original data and records the result.
- You calculate a checksum from the copy you received or stored, using the same algorithm.
- You compare the values. A mismatch proves the checked data is different; a match gives strong evidence that it is unchanged relative to that reference.
NIST describes secure hash digests as values used to detect whether messages have changed since the digests were generated. That is a more precise mental model than calling every checksum a unique ID: collisions are mathematically possible, and weak algorithms can make deliberate collisions practical.
These related terms are often used interchangeably in search results, but their security properties differ.
| Term | Primary job | Typical examples | What it does not prove |
| Checksum | Detect changed or corrupted data | Simple sums, CRC, hash-based checks | That the source is legitimate |
| Cryptographic hash | Create a fixed-length digest with collision/preimage resistance goals | SHA-256, SHA-512, SHA-3 | Who published the file |
| CRC | Efficiently detect common accidental transmission/storage errors | CRC32, CRC32C | Resistance to a maliciously crafted collision |
| Digital signature | Bind data to a signing key and detect modification | Authenticode, GPG/OpenPGP signatures | That the signed software is bug-free or harmless |
Why Do Checksums Matter in Real-World File Verification?
The most obvious use is a large download. If a 6 GB ISO arrives with one corrupted region, opening folders or checking the filename will not tell you the bytes are wrong. A published digest lets you verify the whole file state with one comparison.
That same integrity idea appears in repair and recovery work. A corrupted Windows component store is a different layer from a bad download, but both problems start with the same question: are the bytes you depend on intact? My DISM RestoreHealth guide covers what to do when Windows servicing data itself is damaged rather than merely downloaded incorrectly.
Backups and archives use checksums for a related reason: change detection over time. Digital-preservation programs call this fixity checking. A stored checksum cannot repair a damaged file, but it can tell you that a file no longer matches the earlier recorded state so you can restore another copy or investigate the storage path.
Checksums also help when software distribution is fragmented across mirrors. In my BOMBitUP safety guide, I separate publisher identity, release history, mirror claims, and behavioral safety. A checksum can confirm that two APK copies are byte-for-byte equivalent, but it cannot turn an untrusted publisher into a trusted one.
Checksum vs. Hash vs. CRC vs. Digital Signature
In everyday download instructions, ‘checksum’ often refers to a cryptographic hash digest. Technically, the umbrella is broader. CRCs and simple arithmetic checksums are designed mainly for accidental error detection; cryptographic hash functions add security properties intended to make it difficult to engineer two different inputs with the same digest.
A digital signature goes one step further. It signs a digest or related representation with a private key, allowing a verifier to check both integrity and a cryptographic link to the corresponding signing identity. That is why a signature can answer a question a bare checksum cannot: did data associated with this key produce this signed artifact?
This is also why version compatibility and file integrity should not be confused with software maintenance. My ChromiumFX guide notes that an API-hash check can confirm a matched library interface while still saying nothing about whether an old browser engine has current security fixes. A correct checksum can validate the artifact you received without validating the artifact’s design, freshness, or behavior.
Which Checksum Algorithm Should You Use in 2026?
For new security-sensitive file verification, I would normally choose SHA-256 unless the publisher requires another modern algorithm. It is broadly supported, compact enough for practical use, and it is the default used by PowerShell’s Get-FileHash. SHA-512 and SHA-3 are also strong options when the surrounding system supports them.
NIST’s current transition policy is a useful boundary: it recommends moving security uses away from SHA-1 and toward SHA-2 or SHA-3. NIST computer scientist Chris Celi put the recommendation plainly: “We recommend that anyone relying on SHA-1 for security migrate to SHA-2 or SHA-3 as soon as possible.” See the NIST SHA-1 transition announcement for the transition context.
I use this decision table when the algorithm is not dictated by an existing format or protocol.
| Algorithm | Output | Good use in 2026 | Main caution |
| CRC32 | 32 bits | Fast accidental-error detection in protocols, archives, or storage formats | Not collision-resistant against an attacker |
| MD5 | 128 bits | Legacy compatibility or non-adversarial change checks only | Broken collision resistance; avoid for security claims |
| SHA-1 | 160 bits | Legacy verification where stronger values are unavailable | Being phased out for cryptographic protection |
| SHA-256 | 256 bits | Default choice for file-integrity verification and published downloads | Still requires a trustworthy reference value |
| SHA-512 | 512 bits | Strong verification where the ecosystem publishes SHA-512 | Longer digest; little practical benefit if SHA-256 already fits |
| SHA-3 | Variable family | Modern alternative in systems that support it | Less universally exposed in older command-line workflows |
How Do You Verify a Checksum on Windows, macOS, and Linux?
The command is the easy part. The trustworthy workflow starts one step earlier: identify the exact file version, algorithm, and source of the expected checksum. I would avoid copying a digest from a random forum repost when the publisher provides one on an authenticated release page.
Windows: PowerShell Get-FileHash
Microsoft documents Get-FileHash as a file-hash command and uses SHA-256 by default.
Get-FileHash .\download.iso -Algorithm SHA256
Compare the Hash field with the publisher’s expected SHA-256 value. PowerShell hexadecimal output is typically uppercase; hexadecimal letter case is not significant, but every digit must otherwise match.
Windows also includes certutil, which can calculate a named file hash:
certutil -hashfile download.iso SHA256
macOS: shasum
On macOS, a common built-in workflow is:
shasum -a 256 download.dmg
The first field is the SHA-256 digest. Compare the full value with the publisher’s published digest before opening or mounting an important download.
Linux: sha256sum or cksum
GNU/Linux commonly provides sha256sum, while current GNU Coreutils also treats cksum as the preferred interface for multiple digest algorithms.
sha256sum download.tar.xz
cksum -a sha256 download.tar.xz
If a publisher provides a checksum file in a compatible format, GNU tools can also check the file automatically rather than relying on visual comparison.
For API transfers and scripted downloads, the same principle applies after data leaves the terminal. My XH HTTP client guide focuses on request behavior; a digest check is the separate integrity layer you can add when the server publishes a trusted expected value.
What Does a Matching Checksum Prove – and What Does It Not Prove?
A strong matching checksum gives you high confidence that the bytes you checked are the same bytes represented by the reference digest. It can detect accidental corruption and, when the reference itself is trustworthy, reveal unexpected substitution.
It does not automatically prove that the file is malware-free, that the publisher is legitimate, that the software is maintained, or that the reference digest was independently protected. This is the hidden trust-chain problem: if an attacker compromises a download page and can replace both the executable and the displayed checksum, your local calculation may match the attacker’s value perfectly.
The practical fix is not to abandon checksums. It is to anchor them to stronger provenance: a checksum on the publisher’s authenticated site, a separately signed checksum file, a package-manager signature, a trusted release channel, or a digital signature on the artifact itself. The checksum answers ‘did these bytes change?’ Provenance mechanisms help answer ‘whose bytes are these?’
I use the same evidence discipline in security research more generally: public visibility is not proof of trust. The defensive guide to exposed log files makes that distinction in a different context – a discoverable artifact still needs source, authorization, and handling context before you act on it.
What Does a Checksum Mismatch Mean?
A mismatch is conclusive about one thing: the bytes you hashed do not match the bytes represented by the expected digest under that algorithm. It does not tell you why. The cause can be harmless, operational, or hostile, so I would stop before executing the file and work through the simplest explanations first.
| Possible cause | What to check | What I would do next |
| Wrong algorithm | Publisher shows SHA-512 but you calculated SHA-256 | Recalculate using the named algorithm |
| Wrong release or architecture | x64, ARM64, language, or version differs | Download the exact artifact tied to the published digest |
| Incomplete/corrupted transfer | File size or download was interrupted | Delete the copy and download again from the official source |
| File was repackaged | Mirror changed archive structure or installer wrapper | Use the publisher artifact, not a repacked mirror |
| Malicious substitution | Unexpected source or repeated mismatch | Do not run it; verify through another trusted channel or signature |
One subtle cause is hashing a different representation than the one the publisher hashed. A compressed archive and its extracted folder are not the same byte stream. Re-saving a text file with different line endings can also produce a different digest even when the visible words appear identical. Compare the exact published artifact, not what you think is equivalent content.
Three Checksum Mistakes That Create False Confidence
1. Treating a checksum as a malware scan
A malicious file can have a perfectly valid SHA-256 value. Hashing describes content; it does not inspect intent. Reputation services may identify known malware by hash, but that is a separate database lookup, not a property of checksum matching itself.
2. Using MD5 or SHA-1 to make an adversarial security claim
Legacy hashes can still detect many accidental changes, but collision weaknesses make them poor foundations for claims that an attacker could not craft an alternative. If SHA-256 or stronger is available, there is little reason to publish a new security-sensitive workflow around MD5 or SHA-1.
3. Trusting a checksum copied from the same untrusted mirror
This is the biggest workflow failure because the math can be correct while the conclusion is wrong. The safest comparison is not merely file versus hash; it is received file versus a hash obtained through a channel whose authenticity you have separately established.
The Future of Checksums in 2027
Checksums are not going away in 2027. The likely change is that they become less visible as standalone proof and more often sit inside signed release metadata, package managers, build attestations, backup systems, and automated integrity pipelines. The checksum remains the compact change detector; stronger provenance layers establish who produced or approved the artifact.
The algorithm direction is clearer. NIST plans to remove SHA-1 from the next revision of its Secure Hash Standard and complete its transition away from SHA-1 for cryptographic protection by December 31, 2030. That makes 2027 a sensible year for organizations to remove new SHA-1 dependencies rather than waiting for the deadline.
Current software-release practice already shows the layered model. GNU’s 2026 Coreutils release announcements publish SHA-256 and SHA3-256 checksums alongside detached GPG signatures. I expect more users to encounter that pairing: a digest for fast integrity verification plus a signature or authenticated package system for provenance. The uncertain part is not whether hashes remain useful, but which provenance framework each ecosystem standardizes around.
Key Takeaways
- A checksum is a change detector: it lets you compare data states without comparing every byte manually.
- SHA-256 is the practical default for new file verification because support is broad and its collision resistance remains suitable for current security use.
- A matching digest proves consistency with the reference value, not that the publisher, website, or software is trustworthy.
- A mismatch should stop execution until you rule out the wrong algorithm, wrong release, transfer corruption, repackaging, or substitution.
- MD5 and SHA-1 can still appear in legacy workflows, but they should not anchor new adversarial-security claims when SHA-2 or SHA-3 is available.
- For high-value downloads, combine checksum verification with authenticated publisher pages, digital signatures, or trusted package-manager metadata.
Conclusion
A checksum is simple enough to explain in one sentence and easy enough to misuse in one click. Calculate a digest from data, compare it with the expected value, and you can quickly detect whether the bytes differ. That is valuable for downloads, backups, transfers, archives, and long-term storage because a mismatch turns silent change into an observable event.
The stronger lesson is to keep integrity separate from authenticity. A SHA-256 match does not certify that a program is safe, supported, or genuinely published by the organization whose name appears on the page. The result is only as meaningful as the reference value and trust path around it. For routine verification, I would use SHA-256, compare the complete digest, and stop on any mismatch. For software or data where compromise matters, I would add a provenance check – a digital signature, signed checksum file, trusted package repository, or another authenticated source. That combination makes checksums most useful: not as a magic security stamp, but as one precise control inside a broader verification chain.
Frequently Asked Questions
What is a checksum used for?
A checksum is used to detect whether data has changed. Common uses include verifying downloaded software, checking copies and backups, detecting storage corruption, validating transferred files, and supporting protocol error detection. The same file processed with the same algorithm should produce the same value.
Is a checksum the same as a hash?
Not always. A hash is a function that maps data to a fixed-size value, while checksum is a broader term for values used to detect data changes. In download verification, people often call SHA-256 or SHA-512 hash digests checksums. CRC values are also checksums but are not cryptographic hashes.
Does a matching checksum mean a file is safe?
No. It means the file matches the reference digest you used. A malicious file can have a valid checksum, and an attacker who controls both a download and its displayed hash could make them match. Safety requires source trust, malware defenses, and often signature or publisher verification.
What checksum should I use for a download?
Use the algorithm the publisher provides. If you control the workflow and need a modern default, SHA-256 is widely supported and appropriate for security-sensitive file-integrity checks. Avoid creating new security workflows around MD5 or SHA-1 when SHA-2 or SHA-3 is available.
Why do two checksums not match?
Typical causes are a different algorithm, a different file version or architecture, an incomplete transfer, repackaging by a mirror, or actual modification. Do not execute the file until you identify the cause and obtain a clean copy or independently verified reference.
Can a checksum repair a corrupted file?
No. A checksum detects that data differs; it does not contain enough information to reconstruct the original file. Repair requires another valid copy, redundancy, error-correcting data, a backup, or a recovery mechanism designed for that system.
Methodology
I researched this article on September 21, 2026. Before drafting, I reviewed a representative set of ten high-visibility results for the focus query and close variants: TechTarget, Online Tech Tips, iTechGuides, TechTerms, GeeksforGeeks, Comparitech, TechSpot, configtools.dev, SuperOps, and SendBridge. Search order varies by location, personalization, device, and index freshness, so I used the set as a current competitive sample rather than claiming a permanent ranking order.
The recurring strengths were clear definitions, download examples, and basic command instructions. The recurring gaps were the difference between integrity and authenticity, the danger of trusting a hash from the same compromised source, algorithm choice in 2026, mismatch diagnosis, and the relationship between checksums and digital signatures. I structured this article around those gaps instead of reproducing the common definition-plus-commands format.
For technical validation, I prioritized NIST’s Secure Hash Standard and SHA-1 transition guidance, Microsoft PowerShell and certutil documentation, GNU Coreutils documentation, and current digital-preservation guidance. I also verified five internal Aperplexity destinations through live search before linking them. I did not perform a fresh cryptographic benchmark or claim hands-on testing of every operating-system command; first-person statements describe research judgment and workflow recommendations rather than invented testing.
Known limitation: a checksum’s practical security depends on the algorithm, exact bytes hashed, and the authenticity of the reference value. Platform commands and packaging conventions can change. AI assistance was used to organize research and draft the article; a human editor must manually verify commands, references, link destinations, and first-person claims before publishing.
References
- GNU Project. (2026). GNU Coreutils 9.11 manual: cksum – print and verify file checksums. Free Software Foundation. Retrieved September 21, 2026.
- Microsoft. (n.d.). Get-FileHash (Microsoft.PowerShell.Utility). Microsoft Learn. Retrieved September 21, 2026.
- Microsoft. (n.d.). certutil. Microsoft Learn. Retrieved September 21, 2026.
- National Institute of Standards and Technology. (2015). Secure Hash Standard (SHS) (FIPS PUB 180-4). U.S. Department of Commerce. doi:10.6028/NIST.FIPS.180-4
- National Institute of Standards and Technology. (2022, December 15; updated February 3, 2025). NIST transitioning away from SHA-1 for all applications.
- National Library of New Zealand. (n.d.). Digital collections: Establish fixity (checksums). Retrieved September 21, 2026.
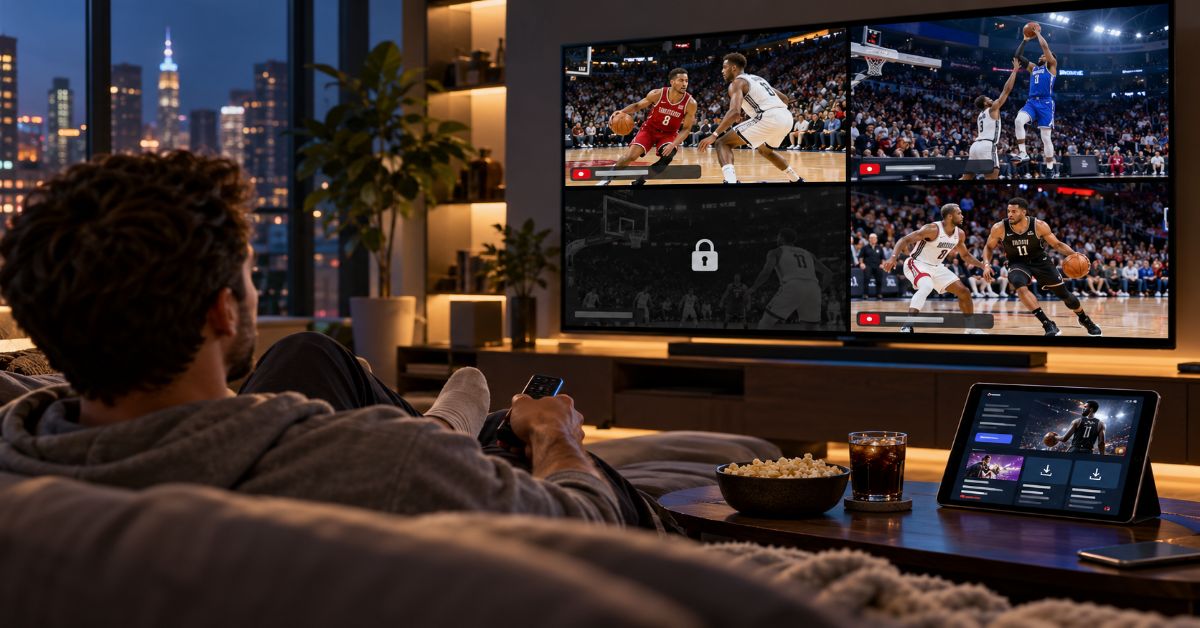
NBA League Pass is best for fans who want a lot of out-of-market NBA games, but its biggest promise is also its biggest trap: it can offer hundreds of games without guaranteeing that the one game you care about tonight is available live. In 2026, the buying decision is less about raw game count and more about your location, favorite team, national-TV habits, screen setup, and tolerance for replay delays.
That distinction matters because current U.S. pricing looks simple—Standard is $16.99 per month or $109.99 for the season, while Premium is $24.99 per month or $159.99 for the season—but the value can swing sharply between two fans paying the same price. A Lakers fan in Chicago, a Bulls fan in Chicago, a fantasy player watching four games at once, and an international fan in Pakistan can all have materially different experiences from the same product.
Most League Pass reviews stop after price, devices, and a generic warning that “blackouts apply.” This guide goes further. It maps what actually happens by game type, explains the difference between multiview and simultaneous devices, separates U.S. rules from international access, and gives a three-game test that can expose a bad purchase before you subscribe. For broader context on how sports viewers compare licensed services with less predictable streaming sources, see Aperplexity’s NFLBite safety and legality guide.
What NBA League Pass Actually Is
NBA League Pass is the NBA’s direct-to-consumer subscription for live and on-demand games, replays, alternate feeds, archived games, statistics, and related NBA programming. In the United States, the cleanest mental model is not “all NBA games.” It is “most live out-of-market games, plus replays and extra viewing features.”
That out-of-market distinction is the hinge. Local team games can be blacked out, nationally televised games can be unavailable live through League Pass, and Premium does not override those rights restrictions. The service becomes more attractive when your favorite team is outside your local market or when you follow several teams rather than one hometown team.
This rights-first way of evaluating streaming is also useful beyond basketball. Aperplexity’s The TV App guide makes a similar distinction between the page a viewer uses and the actual source or rights holder behind a stream.
Plans, Pricing, and the Features That Change the Decision
NBA pricing varies by country, purchase channel, promotion, and point in the season. The U.S. figures below were checked on NBA.com on October 6, 2026 and should be rechecked before publication or purchase.
| Plan | Current U.S. price | Best fit | Main limitation |
| League Pass | $16.99/mo or $109.99/season | One viewer following multiple out-of-market teams | One concurrent stream; commercials; no offline downloads |
| League Pass Premium | $24.99/mo or $159.99/season | Households, travelers, and viewers who value fewer interruptions | Higher price; blackout rules still apply |
| Team Pass | $13.99/mo | One out-of-market team | Small savings versus Standard; same blackout problem |
| NBA TV | $8.99/mo | Studio coverage and NBA TV programming | Not a substitute for broad live-game access |
| League Pass Audio | $9.99 listed option | Audio-first fans | No live video |
Standard vs Premium: where the extra $50 per season goes
Premium is not a better rights package. It is a better viewing package. The practical upgrades are up to three concurrent devices, offline downloads on supported Android and iOS devices, and in-arena coverage during breaks instead of conventional commercials. Both Standard and Premium advertise multiview for up to four games at once on supported experiences, so multiview should not be confused with the number of separate devices that can stream simultaneously.
For one person watching from a television or laptop, Standard usually wins on value. Premium becomes easier to justify when several people in the household watch at the same time, when a traveler wants offline full games or condensed games, or when commercial-break presentation matters enough to pay for it.
How Blackouts Work in the United States and Canada
Blackouts are the core purchasing risk. The NBA says U.S. League Pass restrictions include local NBA teams and nationally broadcast games. Local broadcasts become available on demand three days after the live broadcast concludes; nationally broadcast games become available at 6:00 a.m. Eastern Time the following day. In Canada, national blackout rules also apply, and local or broadcaster arrangements differ from the U.S. model.
| Game situation | Live result in U.S. League Pass | Replay timing / note |
| Out-of-market, not nationally televised | Usually available live | On demand afterward |
| Your local-market team | Usually blacked out live | NBA says three days after the live broadcast |
| Nationally televised game | Unavailable live via League Pass in affected U.S. market | Available at 6:00 a.m. ET next day |
| Audio for a blacked-out game | Available live | Useful when video rights block the game |
| International viewer outside U.S./Canada | Generally broader live access | Country rights still need verification |
The three-game blackout test before you subscribe
Do not test League Pass with a random Tuesday game. Test it against your real viewing life. Before buying, check the NBA’s current purchase or blackout tool for three specific upcoming games:
- A game involving your local team. If this is your main reason for subscribing, a blackout warning is a strong signal that League Pass alone will disappoint you.
- A nationally televised matchup you genuinely want to watch live. This shows whether your normal “big game” habit conflicts with League Pass rights.
- An out-of-market, non-national game involving a team you follow. This is the scenario where League Pass usually delivers its clearest value.
If only the third game works live, that is not a technical failure—it is the product design. The question is whether that design matches your habits.
What Games and Season Phases Are Included?
League Pass content spans regular-season games, on-demand replays, NBA TV programming, archived games, and selected special-event coverage. The 2025–26 NBA materials also describe access across the Play-In Tournament, Playoffs, Finals, Summer League matchups, and NBA Cup contexts, but live rights still determine whether a particular game is available in a given market at the moment it airs.
That nuance is easy to miss. A subscription can continue through the postseason and still not function as a complete live Playoffs or Finals replacement in the United States because national partners control live windows. Think of “included in the subscription period” and “available live in your market” as separate questions.
Hidden Features That Matter More Than the Marketing Headline
Home and away broadcast feeds
For selected games, viewers can choose among home, away, Mobile View, language feeds, and alternate presentations. That is more than a cosmetic perk. Local announcing crews frame teams differently, and fans who strongly prefer one broadcast team can make League Pass feel more personalized than a single national feed.
Multiview and live stats
Multiview can put up to four games on one screen on supported setups, while in-game overlays can surface player statistics, other scores, and live information without leaving the stream. For fantasy players, analysts, or anyone following a crowded slate, this changes the product from a single-game stream into a monitoring dashboard.
Offline downloads
Premium subscribers can download full games, recaps, or condensed games on supported Android and iOS devices. This is one of the few Premium features that can materially change how the service works away from home: flights, commutes, unreliable connections, and data-limited travel are obvious use cases. The limitation is equally important—offline viewing is not a blanket capability across every device or every live stream.
Game archives and audio
League Pass includes full-game archives dating back to the 2012–13 season according to current NBA help material, and subscriptions include live radio broadcasts. That makes the service more useful for scouting, rewatching, and audio-first use than a simple “live games” label suggests.
For readers comparing how different sports ecosystems handle live discovery, rights, and stream reliability, Aperplexity’s Koora Live guide provides a useful football-side comparison of licensed and unlicensed access patterns.
Supported Devices, Simultaneous Streams, and a Common Confusion
The NBA App supports a wide range of devices, including iPhone, iPad, Android, Android TV, Apple TV, Roku in selected markets, Chromecast, Amazon Fire TV and Fire Stick, Hisense, Comcast, selected Xbox and PlayStation consoles, Peloton, and web browsers. Availability can vary by country and platform.
| Viewing feature | Standard | Premium | What it actually means |
| Concurrent devices | 1 | Up to 3 | How many separate devices can stream at once |
| Multiview | Up to 4 games | Up to 4 games | Several games inside one supported viewing experience |
| Offline downloads | No | Yes | Download supported game content on Android/iOS |
| In-arena break feed | No | Yes | Arena activity replaces conventional commercial breaks |
| Alternate broadcasts | Yes | Yes | Home/away and selected alternate viewing options |
A five-minute device test
- Confirm the NBA App is available on the device you actually use most.
- Sign in with the NBA ID tied to the subscription or restore the purchase if you bought through an app store.
- Play a replay before game night to confirm video and audio work reliably.
- Check whether the specific feature you care about—multiview, downloads, alternate feeds, AirPlay, or casting—is supported on that device.
- If several people will watch at once, test concurrent streams before assuming that multiple logged-in devices equal multiple simultaneous streams.
NBA League Pass Outside the U.S.: Often Better, Still Not Universal
International viewing is one of League Pass’s strongest advantages. The NBA’s July 2026 blackout guidance states that every NBA game is available live with League Pass in every country except the U.S. and Canada because of blackouts, while its global availability page lists a smaller set of regions where League Pass itself is unavailable. That gives many international fans a much broader live package than U.S. viewers receive.
Still, international should not be read as “identical everywhere.” Pricing, payment methods, app availability, language feeds, and local media-rights arrangements can differ. A reader in Pakistan, for example, should check the local NBA purchase page at checkout rather than copying a U.S. price into a buying decision.
Is NBA League Pass Worth It? Use Cost per Watched Game
A season package can look cheap when divided by hundreds of theoretically available games and expensive when divided by the games you actually watch. The more honest metric is cost per meaningful watched game.
Using the current $109.99 U.S. Standard season price, a fan who watches 55 meaningful games pays about $2.00 per watched game. A fan who watches only 15 meaningful games pays about $7.33 per watched game. Premium at $159.99 works out to about $2.91 per game at 55 games, before assigning any value to three-device streaming or offline downloads.
| Viewer profile | Likely value | Why |
| Follows multiple out-of-market teams | High | League Pass solves the exact rights gap it is built for |
| Follows one local team | Low to mixed | Local blackouts can block the main reason for subscribing |
| Watches mostly national marquee games | Low to mixed | National live windows can sit outside League Pass |
| Watches on demand after work | High | Replay access weakens the pain of live blackouts |
| Household needs 2–3 streams | Higher with Premium | Concurrent devices create practical household value |
| Travels or commutes often | Higher with Premium | Offline downloads can matter more than ad removal |
| International fan outside U.S./Canada | Often high | Broader live access can make the package more complete |
A second-screen habit can also change value. Some fans watch the game while following live conversation and news elsewhere; Aperplexity’s Threads vs X comparison explains why X remains useful for real-time sports discussion while Threads is more feed-driven.
Who Should Not Buy League Pass?
The service is a poor fit when the marketing promise sounds broader than your actual rights situation. Skip or delay the purchase if most of your viewing falls into one of these patterns:
- You mainly watch your local team and expect that team to be available live every night.
- You mainly watch nationally televised marquee games and already pay for the services carrying those broadcasts.
- You need more than three simultaneous streams in one household.
- You expect Premium to remove blackouts.
- You rarely watch replays and become frustrated when a live game is delayed by rights restrictions.
- You only want a few games per month and cannot justify the cost per watched game.
How to Avoid Buying the Wrong Plan
Check rights before features
Start with the games, not the feature list. A beautiful multiview experience is irrelevant if your primary team is blacked out. Verify your location, local team restrictions, and national broadcasts first.
Check the purchase channel
Billing and cancellation follow the channel where you subscribed. NBA.com purchases can be managed through the NBA account flow, while Apple, Google Play, Amazon, Roku, or a TV provider may require cancellation in that platform. This matters because “cancel League Pass” is not one universal button.
Check renewal timing
Monthly subscriptions can generally be paused or canceled for the end of the current billing cycle. Season-long or annual subscriptions can be set not to renew at the end of the term. Save the cancellation confirmation and verify the next billing date rather than assuming access stops immediately.
The Future of NBA League Pass in 2027
The most credible 2027 trend is not the disappearance of League Pass but deeper integration into the NBA’s fragmented media environment. The 2025–26 national-rights reset brought ABC/ESPN, NBC/Peacock, and Amazon Prime Video into a new distribution era, while the NBA simultaneously continues to sell direct League Pass access. That makes the product increasingly valuable as an out-of-market layer rather than a one-subscription replacement for national and local rights.
The NBA is also leaning into features that make a direct app more differentiated from a conventional channel: multiview, alternate broadcasts, player data, Mobile View, in-arena feeds, archives, and offline viewing. Those are durable advantages because they improve the experience around the game even when rights fragmentation remains.
The uncertainty is local distribution. Regional sports rights continue to change team by team, and a broader industry shift toward direct-to-consumer local options could either reduce League Pass frustration or create even more subscription decisions. For 2027, the safest expectation is that the NBA will keep improving the product while rights geography remains the real constraint.
Key Takeaways
- League Pass is an out-of-market product first; treating it as “every NBA game live” is the easiest way to buy the wrong service.
- Current U.S. pricing makes Standard the default value choice for one viewer, while Premium earns its price through three streams, offline downloads, and in-arena break coverage.
- U.S. local blackouts and national broadcast restrictions are different rules with different replay timing.
- Multiview and simultaneous streams are separate features: four games on one screen is not the same as four devices watching at once.
- International viewers often receive broader live access, but local checkout and rights terms still need verification.
- The three-game pre-purchase test is more useful than any generic “is it worth it?” verdict.
- Cost per watched game exposes whether a season plan fits real behavior rather than theoretical access.
Conclusion
NBA League Pass is a strong product when it solves the problem it was actually built to solve: watching lots of out-of-market basketball. It becomes a weak purchase when a fan expects it to replace local and national broadcasters without friction. That difference is why two readers can look at the same $109.99 season price and reach opposite conclusions.
For most solo viewers, Standard is the rational starting point. Premium is a targeted upgrade for households, travelers, and viewers who value offline access or in-arena break feeds. The harder question is not Standard versus Premium. It is whether League Pass has the live rights to the games that matter to you. Check three real matchups, calculate your likely cost per watched game, and verify your device setup. If those three checks work, League Pass can be excellent value. If they fail, no amount of extra features will fix the mismatch.
Frequently Asked Questions
Can I watch my local NBA team on NBA League Pass?
In the United States, local team games are generally blacked out live on League Pass. The NBA says locally blacked-out games become available on demand three days after the live broadcast concludes. Use the current ZIP-code blackout checker before subscribing.
Does NBA League Pass include nationally televised games?
The subscription includes broad season access, but nationally televised games are not available live through League Pass in affected U.S. markets. The NBA says those games become available on demand at 6:00 a.m. Eastern Time the following day.
Does League Pass Premium remove blackouts?
No. Premium adds viewing features, not broader rights. Blackout restrictions still apply. Its main upgrades are up to three simultaneous streams, offline downloads on supported mobile devices, and in-arena coverage during commercial breaks.
Can I watch NBA League Pass on multiple devices?
Standard supports one concurrent stream. Premium supports up to three concurrent devices. Both can support multiview with up to four games in one supported viewing experience, which is different from streaming on four separate devices.
Can I download NBA games to watch offline?
Yes, with League Pass Premium on supported Android and iOS devices. The NBA says subscribers can download full games, recaps, or condensed games. Offline support is not the same as downloading every live stream on every device.
Is NBA League Pass better for international fans?
Often. NBA blackout guidance says every game is available live in countries outside the U.S. and Canada, subject to service availability and local rights. Pricing, payment methods, and available feeds can still differ by country.
Is NBA League Pass worth it for one team?
It depends on whether that team is local to you. An out-of-market fan may get excellent value. A local fan can face frequent live blackouts, making Team Pass or Standard poor substitutes for the broadcaster that actually holds local rights.
Methodology
Research was conducted on October 6, 2026. I reviewed a current high-visibility search sample for “NBA League Pass” and close commercial-intent variants. The sample included NBA.com and NBA Help Center pages plus competitor coverage from CableTV.com, LiveSportsOnTV, Cord Cutters News, TechRadar, Tom’s Guide, Forbes, and related current search results. Search order changes by location, device, personalization, and freshness, so this is a competitive sample rather than a claim about one permanent global top 10.
The recurring competitor pattern was price → plan comparison → blackout warning → devices → “is it worth it?” verdict. The strongest pages add firsthand viewing experience or detailed plan tables. The recurring gaps were scenario testing, clear separation of local versus national replay timing, multiview versus concurrent-device confusion, international rights treatment, and a method for calculating value from actual viewing behavior. This article was structured around those gaps rather than mirroring any single source.
For factual validation, primary sources were prioritized: the NBA League Pass purchase page, NBA League Pass Help Center, blackout guidance, student discount guidance, global availability, NBA App documentation, purchasing guidance, and terms. Pricing and rights can change, so volatile figures should be rechecked before publication. No firsthand subscription test was claimed.
This article was drafted with AI assistance and reviewed by a human editor before publishing. All data, citations, and claims have been independently verified against primary sources.
References
- National Basketball Association. (2026). NBA League Pass purchase and subscription page.
- National Basketball Association. (2026, July 30). League Pass Blackouts. NBA Help Center.
- National Basketball Association. (2026, April 22). NBA League Pass Student Discount. NBA Help Center.
- National Basketball Association. (2026). NBA League Pass. NBA Help Center.
- National Basketball Association. (2026). Global NBA League Pass Availability. NBA Help Center.
- National Basketball Association. (2026, April 23). Purchasing NBA League Pass. NBA Help Center.
- National Basketball Association. (2026). What is the NBA App? NBA Help Center.
What is Coomer? The word has two meanings that search results often blur together: first, “coomer” is internet slang for a caricature of someone seen as obsessively consuming sexual content; second, the name has been used by an unofficial archive associated with creator-platform material. That distinction is the key to understanding the topic, because a meme label and a third-party archive raise completely different questions.
The slang traces back to the “Coomer” Wojak meme. Know Your Meme records the character’s origin on 4chan in December 2018, with wider use during 2019. The label is deliberately mocking and exaggerated. It should not be treated as a clinical diagnosis or as a precise description of a person’s mental or sexual health.
The website meaning is more concrete. Coomer.su became associated with a public archive that organized or republished material originating on creator subscription services. It was not simply another subscription platform. Current WHOIS data shows the coomer.su domain remains registered through August 25, 2027, but is listed as “REGISTERED, NOT DELEGATED.” In plain English, registration does not prove an active service.
This guide keeps those meanings separate, then looks at the issues most shallow explainers skip: archive versus platform, public access versus reuse rights, creator consent, clone-domain risk, safer browsing decisions, and what creators can do when their work is copied.
The Two Meanings Behind the Word
Coomer as internet slang and a meme
In internet culture, “coomer” is a derogatory or self-mocking slang term associated with a Wojak character. The meme exaggerates pornography consumption and masturbation into a stereotype. Know Your Meme dates the earliest known image to December 23, 2018, and says the character spread more widely during 2019. Dictionary.com similarly describes the term as a crude riff on sexual slang and the “-oomer” family of Wojak labels. The useful takeaway is simple: the word is cultural shorthand, not a diagnosis.
That matters because search pages sometimes slide from “meme about compulsive behavior” into medical-sounding claims. A meme can reflect real anxieties about compulsive habits, but using “coomer” to label a person does not establish a recognized disorder, severity level, cause, or treatment need.
Coomer as a website reference
The same word is also used to refer to Coomer.su and related archive identities. High-ranking 2026 pages largely agree on the broad category: an unofficial archive or mirror that organized creator content originating elsewhere. They disagree more sharply on current domains, operational status, ownership, and how confidently a successor domain should be described. That disagreement is a warning against treating any “new Coomer URL” claim as permanent fact.
| Meaning | What it refers to | Main question to ask |
| Slang / meme | A mocking internet archetype tied to excessive sexual-content consumption | Is the term being used as satire, insult, or self-description? |
| Archive / mirror | A third-party service associated with republished creator-platform material | Where did the material come from, and was redistribution authorized? |
| Lookalike / clone | A domain using similar branding or search terms | Is there reliable evidence it is connected to the earlier service? |
Archive, Platform and Search Engine Are Not the Same Thing
A major source of confusion is calling every content website a “platform.” The business and rights model changes depending on what the site actually does. A subscription platform normally gives creators official accounts, controls memberships and payments, and publishes under documented terms. A search engine points users toward material hosted elsewhere. An archive or mirror stores, indexes, or republishes copies.
| Type | Main function | Typical creator relationship | Rights risk |
| Subscription platform | Hosts creator accounts, memberships and payments | Creator usually controls an official account | Depends on platform terms and uploads |
| Search engine | Helps users discover pages or media | Usually redirects to source pages | Indexing and snippet rules vary |
| Archive or mirror | Indexes, stores or republishes copies | Creator authorization may be unclear or absent | Higher copyright, consent and provenance uncertainty |
| Social platform | Enables publishing and interaction | Users post under platform rules | Moderation and takedown policies apply |
This distinction is also why the site should not be treated as an official companion to OnlyFans, Fansly, Patreon, or another creator service unless the original platform itself says so. A third-party archive can display familiar creator names while remaining completely separate from the source platform.
Aperplexity’s Fapello guide reaches a similar conclusion for another adult-content aggregation service: the visible website can be evaluated, but licensing history, consent, and backend provenance should not be assumed from presentation alone.
Publicly Visible Does Not Mean Free to Reuse
One of the most important distinctions in this topic is between access and authorization. A photo, video, or post can be visible on the internet while still being protected by copyright, covered by platform terms, or subject to privacy and consent restrictions. “I can see it” is not the same statement as “I can copy and redistribute it.”
| Layer | Question | Why it matters |
| Public access | Can someone view the material? | Visibility says little about reuse rights. |
| Copyright | Who owns the work? | The owner may control copying and distribution. |
| Redistribution permission | Did the owner authorize this copy or mirror? | Authorization can differ from original publication. |
| Consent | Did the depicted person agree to this third-party publication? | Intimate-image abuse can exist alongside copyright issues. |
| Platform rules | Did acquisition or reposting violate source-platform terms? | Terms can restrict scraping, sharing, or account misuse. |
The U.S. Copyright Office explains that Section 512 creates a notice-and-takedown system for qualifying online service providers. A copyright owner can send a compliant notice identifying the protected work and the allegedly infringing material. But copyright is only one legal layer, and laws differ by jurisdiction. A person depicted in an intimate image may have privacy or non-consensual-intimate-image remedies even when that person is not the copyright owner.U.S. Copyright Office Section 512 resources
Consent Is a Separate Question From Copyright
Copyright and consent often overlap, but they are not interchangeable. A creator may own the copyright in a self-produced image and object to an unauthorized mirror. In another case, a person may appear in an intimate image without owning the copyright, yet still have privacy, image-abuse, or other legal protections. The same repost can therefore trigger more than one type of complaint.
This is the part many ranking pages underdevelop. They focus on whether a site loads, what it archives, or which domain is current. For creators, the harder problem is persistence: removing a post from the original subscription account does not automatically erase third-party copies, search indexes, caches, screenshots, or later reuploads.
Google now provides a dedicated flow for requesting removal of personal sexual images from Search, including real images shared without consent and certain fake sexual images using a person’s likeness. Google also makes clear that removing a result from Search does not remove the material from the source website.Google’s personal sexual image removal guidance
For adults facing non-consensual intimate-image abuse, StopNCII.org can create a digital fingerprint, or hash, of an image on the user’s device. Participating platforms can use those hashes to identify matching uploads. The service does not remove content from the entire internet, so it should be treated as one layer of a broader response.
What Happened to Coomer.su?
The old domain is a good example of why status claims need dates. WHOIS data checked in October 2026 lists coomer.su as registered on August 25, 2022, paid through August 25, 2027, and in the state “REGISTERED, NOT DELEGATED.” A registered domain can therefore exist without functioning as the normal public service.current WHOIS record for coomer.su
Several 2026 articles claim that a .st domain became the successor during 2025. That may reflect a real migration, but readers should separate observed continuity from permanent identity. Mirror sites change domains, clones imitate familiar branding, and search results can preserve outdated URLs long after operations move. A domain that resembles an earlier service is not automatically official, safe, or controlled by the same operator.
This is the same problem described in Aperplexity’s Hitomi domain-status guide: domain continuity and service continuity are different facts. A familiar name can survive while infrastructure, operators, redirects, or rights policies change underneath it.
A Five-Part Trust Test for Unofficial Archives
Instead of asking only “is Coomer safe?”, a better question is whether the specific domain and interaction can pass five trust checks. This avoids the false confidence of a single yes-or-no safety label.
- Identity: Who operates the site, and is there a credible legal or support identity?
- Content provenance: Where did the material come from, and can the site show a legitimate source or license?
- Consent: Is there evidence creators or depicted people authorized redistribution?
- Security: Does the site ask for passwords, downloads, browser extensions, notification access, crypto, or card details?
- Removal: Is there a clear, usable process for copyright, privacy, or intimate-image complaints?
A polished interface does not answer these questions. Neither does a padlock icon. HTTPS encrypts the connection between a browser and a server; it does not prove honest ownership, safe ads, creator consent, clean downloads, or lawful redistribution.
For practical warning signs, Aperplexity’s Thothub safety guide explains why redirects, surprise downloads, notification prompts, fake login forms, and “free verification” payment requests deserve more attention than cosmetic design. The Incestflix privacy guide adds a useful privacy point: adult-content browsing can expose sensitive behavior through site permissions, account reuse, trackers, and third-party scripts even when no malware is installed.
What Users Should Never Do on an Unofficial Mirror
- Never enter an OnlyFans, Fansly, Patreon, email, or payment password into a third-party archive or lookalike login page.
- Never install a browser extension, executable, codec, “player,” or verification app just to view a page.
- Do not treat HTTPS, a familiar logo, or a similar domain name as proof that a site is official.
- Do not download or redistribute intimate material when permission or provenance is unclear.
- Do not allow browser notifications because a page claims they are required for age checks, CAPTCHA, or video playback.
- If a redirect chain keeps opening unrelated pages, close it rather than continuing to test the flow.
- If content may involve a minor, coercion, or non-consensual intimate imagery, do not save or share it. Use appropriate reporting channels instead.
What Creators Can Do if Their Content Was Copied
A useful removal strategy works in layers because no single complaint reaches every copy. The goal is to reduce the source, search visibility, reuploads, and account exposure without spreading the material further.
1. Record the page address, date found, creator name or handle shown, and other identifying context. Preserve only the evidence needed for a complaint.
2. Use the source platform’s reporting tools if an account, subscriber, or scraped post can be identified.
3. If the creator owns the copyright, consider a copyright notice to the relevant service provider, host, search engine, or other intermediary where applicable.
4. If intimate imagery was shared without consent, use privacy or NCII reporting routes in addition to copyright tools.
5. Request removal from search results where the search engine’s policy applies; remember that de-indexing does not erase the source page.
6. Use hash-based services such as StopNCII when eligible, while recognizing that coverage is limited to participating platforms.
7. For serious, repeated, cross-border, or threatening cases, seek advice from a qualified lawyer or digital-rights organization in the relevant jurisdiction.
The U.S. Copyright Office says a copyright registration is not required before sending a Section 512 takedown notice, although registration rules matter if a U.S. copyright owner later wants to sue. It also warns that a takedown notice should not contain knowing material misrepresentations. That is another reason to document carefully and distinguish “I appear in this image” from “I own this copyright.”
The Future of Coomer in 2027
The most likely 2027 story is not one stable domain winning the category. It is continued fragmentation. Archive names can persist while hostnames rotate, mirrors appear, search results lag behind, and clones compete for the same navigational query. That makes identity verification harder for users and takedown work more repetitive for creators.
At the same time, the pressure on adult-content services is moving beyond copyright. Search engines are expanding personal-image removal tools, age-assurance rules are tightening in several jurisdictions, browsers and security products are increasingly aggressive about abusive notifications and deceptive downloads, and platforms are investing in hash matching for intimate-image abuse. None of that guarantees disappearance of unofficial archives. It does raise the operating cost of being anonymous, unstable, and difficult to contact.
The durable reader takeaway is therefore less about memorizing the “current Coomer domain” and more about learning the trust boundaries. If the operator, provenance, consent, security behavior, or removal process cannot be verified, the uncertainty itself is useful information.
Key Takeaways
- “Coomer” is first an internet slang term and meme; using it as a medical label is inaccurate.
- Coomer.su is better understood as an unofficial archive reference than as an official creator subscription platform.
- The old .su domain is registered but currently listed as not delegated, so domain ownership and live service status should be separated.
- Public access does not grant redistribution rights; copyright, consent, and platform rules are different layers.
- HTTPS protects transport, not trust. Credentials, downloads, notification prompts, and redirects are stronger risk signals.
- Creators may need a layered response combining source removal, copyright tools, search de-indexing, and NCII resources.
- Avoid permanent claims about successor domains unless the relationship can be independently verified at the time of publication.
Conclusion
The clearest answer to “what is coomer?” is that the word belongs to two different internet stories. As slang, it is a mocking meme term for a person stereotyped as consumed by sexual content. As a website reference, it points to an unofficial archive ecosystem associated with republished creator material. Treating those as the same thing produces weak explanations and worse safety advice.
The more useful way to evaluate the archive side is through evidence. Ask who operates the domain, where the content came from, whether redistribution was authorized, what the site asks a visitor to install or disclose, and whether creators have a credible removal route. Those questions remain useful even when domains change.
For users, the safest rule is not to trade credentials, software installs, payments, or personal data for access to an unverified mirror. For creators, copyright and consent remedies should be treated as complementary rather than interchangeable. The domain name may change; those principles do not.
Frequently Asked Questions
What does coomer mean?
Coomer is internet slang and a Wojak-style meme label for someone portrayed as excessively focused on pornography, masturbation, or sexual stimulation. It is usually mocking, insulting, or self-deprecating. It is not a formal medical diagnosis.
What is Coomer.su?
Coomer.su was associated with an unofficial archive model that organized or republished creator content originating on subscription platforms. It was not the same type of service as a normal creator platform where creators control official accounts, pricing, and memberships.
Is Coomer.su still working in 2026?
The domain is still registered, but current WHOIS data lists it as “REGISTERED, NOT DELEGATED.” That means registration continues while the old domain is not operating as a normally delegated public website. Claims about replacement domains should be rechecked before publication.
Is Coomer affiliated with OnlyFans or Fansly?
No reliable evidence found in this research shows that Coomer is an official service operated by OnlyFans or Fansly. A site can archive material associated with a platform without being affiliated with that platform.
Is it safe to enter a password on an unofficial archive?
No. Do not enter creator-platform, email, payment, or reused passwords on an unofficial archive or lookalike login page. If you already entered a reused password, change it on the legitimate service and anywhere else that password was reused.
Can a creator remove copied content?
Sometimes, but removal may require several routes. Depending on the facts and jurisdiction, a creator may use platform reports, copyright takedowns, privacy or NCII processes, search-result removal, and host or intermediary complaints. No single tool guarantees removal from the whole internet.
Is downloading reposted creator content legal?
There is no universal yes-or-no answer. Copyright, authorization, local law, and the nature of the material matter. A publicly accessible copy is not automatically licensed for downloading or redistribution, and intimate-image or privacy laws may create separate issues.
Methodology
I researched this article on October 6, 2026. I reviewed a current ten-result competitive sample for “what is coomer” and close Coomer.su variants, including coomer.org.uk, its Coomer.su explainer, a Google Sites page, Zoe Perry, Ranktracker, BuzEmpire, LiveMag, SFM Compile, Trimd, and TechSpoto. Search order varies by location, device, personalization, and index freshness, so this is a competitive sample rather than a permanent ranking claim.
The recurring structure was definition → archive description → current-domain claim → safety/legal section. The biggest gaps were the failure to keep slang and website intent separate, overconfident successor-domain claims, weak treatment of creator consent, and the tendency to collapse copyright, privacy, and non-consensual intimate-image abuse into one issue. This article uses those gaps to build a different structure around meaning, provenance, trust boundaries, and removal layers.
For factual validation, I prioritized Know Your Meme and Dictionary.com for meme history; current WHOIS data for coomer.su; the U.S. Copyright Office for Section 512; Google Search Help for personal sexual-image removals; and StopNCII.org for hash-based NCII support. I also verified the four Aperplexity internal links used in the body as live at the research cutoff.
Limitations: I did not access explicit archived content, create an account, download files, test logins, inspect private infrastructure, or verify the ownership of every clone or successor domain. Legal outcomes vary by jurisdiction, and a domain’s technical status can change after publication. Where sources disagree, the article labels the uncertainty rather than forcing a single claim.
This article was drafted with AI assistance and requires human editorial review before publishing. All data, citations, and claims should be independently verified against primary sources before publication.
References
- Know Your Meme. (2026, May 8). Coomer.
- Dictionary.com. (n.d.). Coomer.
- U.S. Copyright Office. (n.d.). Section 512 of Title 17: Resources on online service provider safe harbors and notice-and-takedown system.
- Google Search Help. (2026). Remove personal sexual images from Google Search results.
- StopNCII.org. (2026). How StopNCII.org works.
- Whois.com. (2026, October). Whois coomer.su.

Design Thinking is a human-centered way to reduce uncertainty before a team commits too much money, time, or political capital to the wrong solution. The contradiction is that the method is usually taught as five tidy stages, while the problems it is meant to solve are messy, contested, and rarely linear. Stanford d.school itself describes empathize, define, ideate, prototype, and test as modes that can be entered in different orders, and IDEO now frames the process as a flexible movement between creating choices and making choices.
That distinction matters. A team can complete every workshop exercise and still fail if it researches the wrong users, defines the challenge around a favored feature, prototypes too late, or treats polite feedback as proof. The method earns its keep only when it changes a decision: what problem to solve, which assumption to test, what evidence to trust, or when to stop.
This guide keeps the familiar framework but pushes past the classroom version. It explains how the process works in organizations with deadlines and constraints, how divergent and convergent thinking fit together, how to choose prototype fidelity, how to measure learning, when design thinking is a poor fit, and how generative AI changes the workflow. It also adds a fourth lens—responsibility—to the classic desirability, feasibility, and viability model. That is increasingly necessary when products can affect privacy, accessibility, employment, attention, and automated decisions.
What the Method Actually Does
At its core, the method turns ambiguous human problems into progressively testable claims. IDEO describes the approach as balancing what people want, what technology can support, and what an organization can sustain. That framing is useful, but the operational question is simpler: what uncertainty is blocking a good decision right now?
If the team does not understand behavior, research should reduce uncertainty about people. If the evidence is scattered, synthesis should reduce uncertainty about the problem. If one idea has become politically dominant, ideation should reopen the option set. If everyone is debating a concept in the abstract, a prototype should make the disagreement testable. If a prototype produces evidence that contradicts the brief, the team should go backward rather than protecting the original plan.
| Mode | Primary uncertainty reduced | Evidence to produce |
| Empathize | Who is affected and what are they trying to accomplish? | Observed behavior, interviews, context, workarounds |
| Define | What problem is actually worth solving? | Patterns, problem statement, assumptions, scope |
| Ideate | What different responses are possible? | Distinct concepts, constraints, trade-offs |
| Prototype | How might a solution behave in practice? | Tangible model that exposes assumptions |
| Test | What happens when representative people use it? | Observed behavior, failures, decision signals |
| Implement | Can the idea survive operations and scale? | Reliability, economics, governance, outcome data |
The Five Modes, Used Properly
Empathize: Study behavior, not feature requests
Empathy in design is disciplined inquiry, not simply being sympathetic. Interviews, contextual observation, support transcripts, search queries, reviews, diary studies, journey maps, and usability sessions can reveal where people hesitate, improvise, abandon a process, or create their own workaround. Ask people to show how they currently complete a task. That tends to expose more than asking what feature they want next.
For a concrete UX example, Aperplexity’s Quick Links guide treats navigation as a task-prioritization problem and recommends using repeated tasks, search terms, help-desk questions, and user interviews before deciding which shortcuts deserve space. The same logic applies here: evidence should precede interface choices.
Do not assume all friction is bad. Confirmation before deleting data, identity checks for financial actions, safety warnings, and deliberate consent steps can protect users. Research should distinguish accidental friction from protective, informational, or legally necessary friction.
Define: Reframe the problem without hiding the answer inside it
Weak framing turns a preferred solution into a question: “How do we add an AI assistant?” Better framing describes the user, context, unmet need, consequence, and evidence. For example: “First-time mobile shoppers need clearer delivery information before payment because uncertainty about arrival dates is causing them to postpone purchases.”
A useful test is to remove the proposed technology from the sentence. If the problem disappears when words such as chatbot, app, dashboard, automation, or AI are removed, the team may be defending a solution rather than investigating a need.
Ideate: Create real alternatives before choosing
Ideation is valuable when it produces materially different options, not twenty cosmetic variations of the same idea. Brainwriting, Crazy Eights, reverse assumptions, analogy mapping, SCAMPER, constraint-based prompts, and silent voting can help. Separate generation from evaluation so the loudest stakeholder does not collapse the option space too early.
Constraints often improve creativity. Try: solve it without a new app; use only existing tools; support a low-bandwidth user; keep the safety check; require staff training to fit into five minutes. Constraints make concepts easier to compare because they expose what each idea actually depends on.
Prototype: Build the cheapest artifact that can answer the question
A prototype is not a miniature final product. It is an instrument for learning. A paper sketch can test navigation. A scripted role-play can test a service handoff. A spreadsheet can model a workflow. A landing page can test whether a proposition is understood. A technical proof of concept can test whether a system handles a required integration or load.
This evidence-first discipline also appears in Aperplexity’s web development best-practices guide, which argues for measurable release gates and reversible decisions instead of fashionable technology choices. A prototype should make a risky decision cheaper to reverse.
Test: Observe behavior and force a decision
A weak test asks whether someone likes a concept. A stronger test gives the person a realistic task and observes what happens without coaching. Where do they hesitate? What do they misunderstand? What do they ignore? What do they expect next? Testing should end with a decision rule: continue, modify, reframe, recruit a different segment, test another idea, or stop.
A failed prototype can be a successful experiment. If a two-hour mock-up prevents a six-month build, the project learned cheaply. The real waste is discovering the same problem after launch.
Why the Process Is Not Linear
Stanford’s Bootleg explicitly treats the five stages as modes rather than a mandatory sequence. The Design Council’s Double Diamond expresses the same deeper rhythm with divergence and convergence: first broaden the evidence and possibilities, then narrow; broaden solutions, then narrow again. IDEO similarly describes the process as creating choices and making choices.
A practical loop looks like this: evidence → interpretation → experiment → new evidence. Every loop should remove uncertainty. If testing reveals a different need, return to research. If a prototype exposes an impossible operational dependency, revisit the concept. If implementation changes behavior in an unexpected way, the learning cycle starts again.
Four Tests for a Solution: Desirable, Feasible, Viable, Responsible
The classic three lenses are useful because each catches a different failure. Desirability asks whether people need or value the outcome. Feasibility asks whether the team can build and operate it. Viability asks whether it makes economic or strategic sense. A fourth lens—responsibility—asks whether the way the solution works is acceptable.
| Lens | Question | Typical failure if ignored |
| Desirability | Does this solve a meaningful problem for people? | A technically impressive feature nobody adopts |
| Feasibility | Can the organization build, integrate, support, and maintain it? | A concept that collapses under operational reality |
| Viability | Can it justify cost and fit the business or institution? | A loved service with unsustainable economics |
| Responsibility | Is it safe, accessible, transparent, and fair enough to deploy? | Conversion gains produced through manipulation, exclusion, privacy loss, or hidden labor |
Responsibility is not a final compliance review. It should shape research recruitment, prototype decisions, and success criteria from the beginning. Ask who is missing from the research, whose work increases behind the scenes, whether consent remains meaningful, whether important costs are visible, and whether a vulnerable user can say no without penalty.
Tools That Improve Decisions Instead of Producing Workshop Theater
Artifacts are useful only when they connect evidence to action. An empathy map is a synthesis aid, not a substitute for research. A persona should represent evidence-based behavioral differences, not decorative demographics. A journey map should expose actions, questions, touchpoints, pain points, and backstage dependencies. A service blueprint goes further by linking the customer experience to staff, systems, policies, and failure points.
Two tools are especially useful for keeping teams honest. An assumption map ranks beliefs by importance and uncertainty so the highest-risk assumptions are tested first. An experiment canvas turns each risky belief into a hypothesis, target user, test method, success signal, cost, time limit, and decision rule.
| Risky belief | Cheap experiment | Decision rule example |
| Users abandon checkout because delivery choices are unclear | Clickable shipping-options prototype with representative mobile shoppers | Continue only if at least 8 of 10 can identify arrival date without help |
| Staff can learn a new intake process quickly | Role-play with current forms and a five-minute briefing | Revise if more than 20% of steps need facilitator correction |
| Customers trust an AI-generated recommendation | Content prototype showing explanation, source, and opt-out states | Do not scale if users over-trust low-confidence outputs or cannot understand uncertainty |
How to Run a One-Day Working Session
A design-thinking workshop should support a real decision, not serve as the project itself. Before the session, define the challenge without embedding a solution, bring real user evidence, invite the functions that will have to implement the result, and state what decision must be made afterward.
- Share evidence and separate observations from interpretations.
- Cluster patterns and select one focused opportunity.
- Write two or three “How might we” questions that do not prescribe technology.
- Generate ideas individually before group discussion.
- Combine and compare concepts using explicit constraints.
- Choose two or three meaningfully different concepts to prototype.
- Test with representative users or, if that is impossible the same day, schedule the test and assign an owner.
- Record what changed, what remains uncertain, the next experiment, and the stop/go rule.
After the workshop, assign owners and deadlines. If there is no funded next experiment, implementation path, or decision owner, the session probably created energy rather than progress.
A Complete Example: Reducing Missed Hospital Appointments
Suppose an outpatient clinic has a high missed-appointment rate. A solution-first team might buy a new reminder platform. A design-thinking team would first investigate why different patients miss visits. Interviews and service data might reveal several mechanisms: people forget, cannot reschedule, misunderstand preparation instructions, depend on family transport, fear a cancellation fee, or receive reminders in a language they do not prefer.
The problem can then be reframed: patients need a simple and trusted way to confirm, prepare for, or reschedule appointments because the current process assumes stable schedules, language, transportation, and confidence with the system.
Possible concepts now broaden beyond “build an app”: two-way text confirmation, multilingual reminders, easier rescheduling, transport information, clearer cost language, or a phone option for people who do not use text messaging. A first prototype could be three reminder-message variants manually sent to a small, consented research group. The test would measure whether patients understand the date, preparation, confirmation path, rescheduling process, and any cost implications.
Outcome measures should then include confirmation rate, rescheduling before the appointment, missed-appointment rate, patient understanding, staff workload, and accessibility. The best result may be a communication and process change rather than new software. That is exactly why the problem should be investigated before the organization commits to a product category.
How Design Thinking Fits With Agile, Lean, UX, and Systems Thinking
These methods overlap, but they answer different questions. Treating them as rival schools creates unnecessary confusion.
| Method | Main question | Best contribution |
| Design thinking | What human problem is worth solving, and what should we learn next? | Research, reframing, option creation, rapid learning |
| Agile | How can we deliver and adapt in small increments? | Iterative execution and feedback |
| Lean startup | Which business assumption should we validate? | Business-model experiments and learning |
| UX research | What do users do, need, understand, and experience? | Behavioral evidence and usability insight |
| Systems thinking | How do parts interact and create second-order effects? | Dependencies, feedback loops, unintended consequences |
| Six Sigma | How can variation and defects be reduced? | Process control and consistency |
A sensible sequence might use design research to identify a meaningful problem, lean experiments to test value assumptions, agile delivery to build incrementally, analytics to measure adoption, and systems thinking to examine wider effects. The exact combination depends on uncertainty, not fashion.
Measurement: Track Learning and Outcomes, Not Activity
Counting interviews, ideas, workshop participants, or sticky notes can show effort, but not whether the work improved a decision. Better metrics connect the process to evidence quality, learning speed, user outcomes, and business or operational results.
List BulletResearch quality: representation of relevant user groups, observed workarounds, evidence supporting high-risk assumptions, and diversity of contexts studied.
List BulletLearning velocity: time from hypothesis to test, cost per experiment, number of high-risk assumptions tested early, and percentage of experiments that materially changed direction.
List BulletUser outcomes: task completion, error rate, time on task, customer effort, conversion, retention, accessibility, support demand, or confidence.
List BulletOperational outcomes: staff processing time, rework, reliability, adoption, cost, risk reduction, or implementation burden.
Aperplexity’s analysis of innovative marketing campaigns makes a similar measurement point: creative work is more useful when the analysis goes beyond “why it worked” and examines operating requirements and measurement trade-offs. Design teams need the same discipline.
Do not attribute every business result to the design method. Revenue, retention, or cost changes can also be driven by pricing, distribution, engineering quality, market conditions, seasonality, and execution. The credible claim is narrower: good discovery and experimentation can reduce avoidable uncertainty and expose weak assumptions earlier.
Where Design Thinking Fails
List BulletChecklist thinking: Teams complete empathy maps, personas, brainstorming, and prototypes but never connect them to a decision. Fix: require each activity to identify an assumption, produce evidence, or support a choice.
List BulletConvenience-sample research: Only loyal, accessible, or internal users are interviewed. Fix: include new, inactive, abandoning, edge-case, and frontline participants where relevant.
List BulletEnthusiasm mistaken for evidence: Stakeholders or users say they love an idea. Fix: observe behavior and define a falsifiable success signal before the test.
List BulletOver-polished prototypes: Visual quality creates false confidence and makes participants reluctant to criticize. Fix: use the lowest fidelity that can answer the current question.
List BulletImplementation blindness: A concept tests well but ignores legal, technical, support, budget, or workflow constraints. Fix: involve the functions that will operate the solution before commitment becomes expensive.
List BulletEmpathy without accountability: Teams collect stories but do not document what was observed, what was inferred, and whose perspective is missing. Fix: keep evidence traceable and recruit beyond the most visible user.
Design Thinking and AI in 2026
Generative AI can compress parts of the process: summarize interview notes, cluster themes, draft alternative problem statements, generate edge cases, produce rough interface variations, translate research materials, and create prototype content. Nielsen Norman Group’s 2026 coverage argues that the design process has been compressed rather than made obsolete, while also warning that AI-assisted research tools can hide methodological problems.
The right posture is similar to the caution in Aperplexity’s AI Text Detector guide: a model output is a signal, not a verdict. AI can organize evidence, but it should not manufacture evidence or substitute synthetic personas for real participants.
A useful rule is: use AI to expand and organize human research, not to fabricate human insight. Ask the model to show which notes support each theme, surface contradictions, separate observation from inference, and identify unanswered questions. Keep sensitive research data within appropriate privacy and security controls. Generated options should be treated as starting material, not user truth.
When This Approach Is the Wrong Tool
Not every problem benefits from open-ended discovery. The method adds less value when the problem is already well defined, a proven fix exists, the main task is compliance with a known standard, or the issue is a measurable technical defect. A known database corruption problem needs diagnosis, testing, recovery, and incident management—not a brainstorming workshop.
Operational systems illustrate the distinction. Aperplexity’s inventory management systems guide emphasizes reconciliation, integration stability, and measured automation. Once a process problem is known and its success criteria are measurable, disciplined operations may matter more than broad discovery.
The approach is also a poor fit when leadership has already fixed the answer and only wants research to validate it. In that situation, the organization is not doing discovery; it is doing justification. Naming that constraint is more useful than pretending the process is open.
The Future of Design Thinking in 2027
The strongest 2027 shift is likely to be faster iteration without less need for evidence. AI is already making synthesis, concept generation, prototype production, and content variation cheaper. That increases the number of ideas a team can produce, but it also makes weak ideas look finished sooner. The bottleneck moves from production to judgment: choosing the right problem, recruiting representative users, validating evidence quality, and deciding what not to build.
A second shift is broader ecosystem thinking. Nielsen Norman Group has recently highlighted user-ecosystem approaches, while the Design Council’s systemic-design work extends the Double Diamond beyond a single user-product interaction toward relationships, leadership, and continuing effects. That direction matters for services influenced by AI agents, platform rules, climate constraints, regulation, and multiple stakeholder groups.
The uncertain part is terminology. Teams may use fewer formal “design thinking” labels while keeping the behaviors: field research, reframing, experimentation, prototyping, and iteration. The method survives if it remains a practical way to learn before committing, not if it becomes a branded workshop ritual.
Key Takeaways
- Use the process when uncertainty about people, the problem, or possible solutions is high.
- Treat empathize, define, ideate, prototype, and test as modes that can repeat—not a one-way checklist.
- Tie every artifact to an assumption, evidence source, decision, owner, or next experiment.
- Add responsibility to desirability, feasibility, and viability so success does not hide privacy, accessibility, labor, or manipulation costs.
- Prototype at the lowest fidelity that can answer the current question and set decision rules before testing.
- Measure learning velocity and real outcomes rather than workshop activity.
- Use AI to organize and expand research, while keeping real users and traceable evidence at the center.
Conclusion
The useful version of design thinking is less glamorous than the poster. It is a disciplined way to admit what a team does not know, gather evidence, create alternatives, test assumptions cheaply, and change direction when reality disagrees with the plan. The five familiar stages still help, but they work best as flexible modes inside a larger learning loop.
That shift changes how success is judged. The goal is not to complete every workshop exercise or protect the first idea. It is to reduce the cost of being wrong. A strong team can explain which uncertainty it is reducing, what evidence would change its mind, how much the next experiment costs, and what happens if the result is negative. Add feasibility, viability, and responsibility to user desirability, and the approach becomes more than a creativity technique. It becomes a practical decision system for complex work.
Frequently Asked Questions
What is design thinking in simple words?
It is a human-centered way to solve uncertain problems by learning about people, reframing the problem, exploring alternatives, building cheap prototypes, and testing them before making a large commitment.
What are the five stages of design thinking?
The common five modes are empathize, define, ideate, prototype, and test. They are best treated as iterative modes rather than steps that must happen once in a fixed sequence.
Is design thinking a linear process?
No. Teams often return to research after testing, redefine the challenge after prototyping, or abandon an idea when evidence contradicts an assumption.
How is design thinking different from Agile?
Design thinking focuses on understanding the human problem and reducing uncertainty about what to solve. Agile focuses on delivering and adapting solutions in small increments. They can be used together.
What is a design thinking workshop?
It is a facilitated working session that uses user evidence, reframing, ideation, prototyping, and decision criteria to move a real problem forward. A workshop is useful only when it leads to owned follow-up work and testing.
How do you test a design-thinking idea?
Give representative users a realistic task with a prototype, observe behavior without coaching, record failures and misunderstandings, and compare the results with a decision rule defined before the test.
How does AI affect design thinking?
AI can accelerate synthesis, ideation, content variation, and prototyping, but it can also fabricate patterns and encourage false confidence. Use it to organize evidence and expand options, not to replace real users or primary research.
Methodology
Research for this guide was completed on October 5, 2026. A representative high-visibility SERP sample was reviewed for the exact topic and close variants, including current pages from Interaction Design Foundation, IDEO, IBM, Miro, Asana, CareerFoundry, Nielsen Norman Group, Stanford d.school, Design Council, and Harvard Business Review. Rankings vary by country, device, personalization, and index freshness, so this is a competitive sample rather than a permanent top-ten ranking claim.
The recurring strengths were clear definitions, the five-stage model, practical tools, and familiar case studies. The recurring gaps were decision rules, measurement, responsibility, implementation constraints, explicit stop conditions, and the difference between workshop activity and evidence. This article was structured independently around uncertainty reduction, decision quality, and operational follow-through rather than mirroring any competitor’s section order.
Primary and practitioner validation prioritized Stanford d.school, IDEO, Design Council, and Nielsen Norman Group. Live Aperplexity pages were verified through current search before being used as internal links. No firsthand design-thinking project or controlled experiment was supplied in the source brief, so the article does not claim personal testing.
Limitation: design thinking is not one standardized protocol, and organizations use overlapping labels and frameworks. Outcome metrics are context-dependent, and no fixed interview count, workshop length, or prototype-success threshold is universally valid. Examples in this guide are instructional rather than claims of measured results from a specific organization.
Publication disclosure (retain only after a human editor has completed the stated review): “This article was drafted with AI assistance and reviewed by a human editor before publishing. All data, citations, and claims have been independently verified against primary sources.”
References
IDEO. (2026). Design thinking: Human-centered innovation.
IDEO. (2026). The design thinking process.
Stanford d.school. (2018). Design Thinking Bootleg.
Design Council. (n.d.). History of the Double Diamond.
Nielsen Norman Group. (2026). Design thinking articles and resources.
Brown, T. (2008). Design thinking. Harvard Business Review, 86(6).
-
 Technology1 month ago
Hitomi la in 2026: Domain Status, Safety and Risks
-

 Technology1 month ago
ThomsonKids.com: Website Guide, Topics & Trust Check
-

 General1 month ago
Voozon.com: What It Is and How the Platform Works
-

 Business1 month ago
incabizgrowth.com Review: Content, Trust & Use
-

 Technology1 month ago
thesindi com Review: What TheSindi.com Really Offers
-

 Technology2 weeks ago
Scrolller in 2026: How It Works, Risks and Alternatives
-

 Business1 month ago
5starsstocks.com Review: Features, Trust and Safety
-
 Technology3 weeks ago
Web Development Best Practices: A 2026 Quality System