Technology
Best Audiobook Apps in 2026: Which One Fits Your Listening Style?

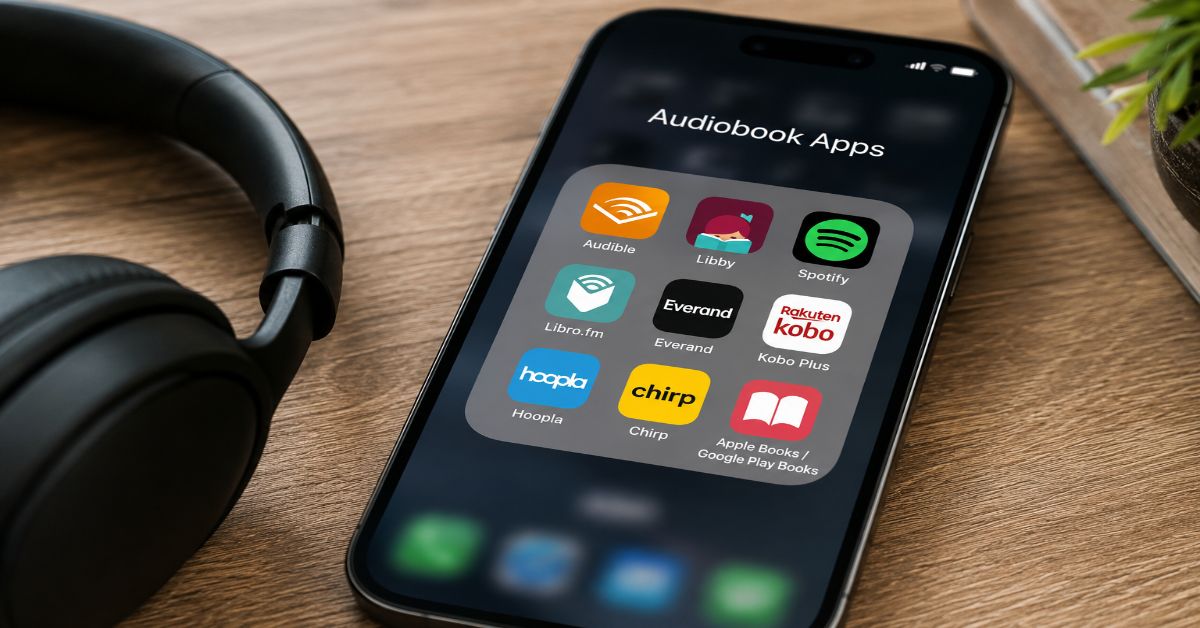
A 14-hour thriller can cost less than lunch, nothing at all or a full monthly subscription depending on where you press Play. The best audiobook apps in 2026 are Audible for premium ownership and broad choice, Libby for free library borrowing, Spotify for casual listening inside an existing Premium plan, Libro.fm for DRM-free purchases that support independent bookshops, Everand and Kobo Plus for subscription value, Hoopla for instant library access, and Chirp for bargain-priced one-off purchases. I compared these services by the rules that actually affect a listener after the sign-up screen: how you pay, whether unused value expires, whether a finished book remains yours, how offline listening works, and what happens when you want a 25- or 30-hour title instead of a short bestseller.
That last point matters more than most rankings admit. A credit-based service charges one credit for an eligible title whether it runs six hours or thirty, while an hours-based plan can make a long fantasy novel consume two months of listening allowance. Library apps reverse the trade-off: the price is unbeatable, but popular releases may involve holds, borrowing limits, or a catalog chosen by your local library. Deal stores avoid subscriptions altogether, but they reward patience rather than giving you every title on demand.
This guide is therefore not a single-winner list. It is a practical match between listening habits and business models. Prices below use U.S. pricing where a current public price is available and were checked against official service pages in August 2026. Availability, taxes, catalogs, and plan rules can differ by country, so treat the pricing as a comparison baseline rather than a universal quote.
What are the best audiobook apps right now?
For most paid listeners, Audible is the strongest all-around choice because its Premium plan combines a monthly credit you can keep with an included streaming catalog. For free listening, Libby is the best first app to install if you have a library card, while Spotify is the easiest value add for people already paying for eligible Premium plans.
How do the best audiobook apps compare at a glance?
This table separates ownership from temporary access, which is the fastest way to see which model matches your habits.
| App | Best for | Pricing model | What happens to the book? |
| Audible | Overall paid choice | $8.99 Standard; $14.95 Premium 1-credit plan | Premium credit purchases are kept; Standard selections require membership |
| Libby | Free library borrowing | Free with a participating library card | Borrowed, then automatically returned |
| Spotify | Existing Premium users | 15 audiobook hours included in eligible Premium plans | Streaming allowance; unused monthly hours expire |
| Libro.fm | DRM-free ownership + indie support | $14.99 monthly for 1 credit in the U.S. | Purchased audiobooks and unused credits remain after cancellation |
| Everand | Audiobooks plus ebooks | $11.99 / $16.99 / $28.99 for 1 / 3 / 5 unlocks | Unlocked books remain available while subscribed |
| Kobo Plus | Low-cost subscription catalog | $7.99 Listen; $9.99 Read & Listen in the U.S. | Access lasts while subscribed |
| Hoopla | No-wait library listening | Free through participating libraries | Borrowed access; limits are set by the library |
| Chirp | Discounted one-off purchases | No subscription; rotating deals can start at $1 | Purchased audiobooks are kept |
| Apple Books / Google Play Books | Pay only when you want a title | Per-title pricing | Purchased titles stay in the account/library |
How I compared these audiobook apps
I used a research-first comparison rather than pretending every listener needs the same feature set. I checked official pricing and help pages for plan structure, catalog claims, expiration rules, library mechanics, offline support, and ownership language. I then compared the services against five practical questions:
- Do I own a purchased title, or am I only renting access while I pay?
- Is the monthly value measured in books, credits, hours, or library borrows?
- What happens to unused credits or hours?
- Can I download titles for offline listening?
- Does the model become expensive or inconvenient for long audiobooks?
That framework produces a different winner for a commuter who finishes one 10-hour book a month than for a fantasy listener who regularly chooses 30-hour epics. It also exposes a hidden cost: expiring time allowances can be more restrictive than their headline price suggests.
Which best audiobook apps are worth using?
Audible: best overall for paid listeners who want ownership
Audible remains the safest default for someone who wants a predictable monthly audiobook and access to a secondary streaming catalog. In the U.S., Audible Standard is listed at $8.99 per month and lets members select one audiobook each month, but that selected title is available only while the membership continues. Audible Premium at $14.95 per month includes one credit, and titles bought with a credit remain yours after cancellation. Premium also includes the Audible Plus Catalog.
The useful distinction is Standard versus Premium, not simply ‘Audible versus everyone else.’ If long-term ownership matters, the Premium credit model is the more durable choice. A single credit can also be unusually valuable on very long or expensive books because the redemption is title-based rather than hour-based.
Best fit: listeners who reliably finish at least one premium audiobook a month, want major releases on demand, or prefer keeping credit purchases in a permanent library.
Libby: best free audiobook app with a library card
Libby is the first app I would recommend to anyone trying to cut audiobook spending. It is free to use with a valid library card, has no subscription fee, no in-app purchase requirement, and no late fees because digital loans return automatically. You can stream or download audiobooks for offline listening, and you can add multiple library cards when you are eligible for more than one system.
The trade-off is availability. Each library selects its own catalog and sets its own loan and hold limits. Popular books can require a wait, although Libby lets you suspend holds without losing your place and gives you 72 hours to act when a hold becomes available. That makes Libby excellent for a flexible reading list and less reliable when you need one specific new release tonight.
Best fit: budget-conscious listeners, library users, and anyone happy to keep a queue of several possible next books.
Spotify: best for casual audiobook listening inside one app
Spotify makes the most sense when you already use it for music and podcasts. Eligible Premium Individual plans and the plan manager on eligible Duo or Family plans include 15 hours of audiobook listening per month from Spotify’s subscriber catalog. Spotify says that catalog contains more than 700,000 audiobook titles in the U.S. Unused included hours expire when the monthly allowance resets.
That hours model is the key limitation. A 10-hour mystery may fit comfortably inside one month, but a 30-hour epic requires more than one base monthly allowance unless you add or buy more listening time. Spotify also offers an Audiobooks Access plan in the U.S. and sells extra audiobook hours, so the service is flexible, but heavy listeners should compare the total cost against a credit-based plan.
Best fit: existing Spotify subscribers who listen casually and value having music, podcasts, and audiobooks in one interface.
Libro.fm: best for DRM-free purchases and independent bookshops
Libro.fm is the strongest Audible alternative for people who care about file flexibility and where their money goes. Its U.S. monthly membership is $14.99 for one audiobook credit. Official Libro.fm support says credits can be used across more than 600,000 audiobooks, never expire, and remain available after you cancel. Members also receive 30% off additional à la carte purchases.
The bigger differentiator is that Libro.fm describes its audiobooks as DRM-free and shares purchase support with the independent bookshop you choose. That gives the service a different kind of ownership story: you are not merely building a library inside one closed app. Regional rights can still make individual books unavailable, so no catalog claim means every title is globally accessible.
Best fit: listeners who want to keep purchases, avoid expiring credits, and support independent bookstores without giving up mainstream audiobook selection.
Everand: best for people who switch between audiobooks and ebooks
Everand is built for format-hopping readers. Its current U.S. plans start at $11.99 per month for one unlock, rise to $16.99 for three unlocks, and reach $28.99 for five. Everand says each unlock can be used on a book from a library of more than 1.5 million books, while a separate unlimited catalog of 20,000-plus audiobooks, ebooks, and podcasts does not require unlocks.
The important ownership caveat is that unlocked books are yours for the duration of the subscription, not permanent purchases. In exchange, Everand combines ebooks and audiobooks in one plan and supports offline use. That can be a better value than an audiobook-only service for someone who reads text on weekdays and listens on commutes.
Best fit: mixed-format readers who value one subscription more than permanent ownership.
Kobo Plus: best low-cost subscription for heavy catalog browsing
Kobo Plus offers one of the clearest low-cost subscription options. Kobo lists Kobo Plus Listen at $7.99 per month in the U.S., with access to more than 150,000 audiobooks, while Read & Listen costs $9.99 and adds an ebook catalog of more than 1.5 million titles. You can add as many eligible Kobo Plus titles as you want and listen in the Kobo app or on supported Kobo devices.
The catch is the word eligible. Kobo Plus is a subscription catalog, not the entire Kobo audiobook store. Kobo also offers a separate monthly audiobook-credit subscription for listeners who want a title from its expanded eligible catalog. This makes Kobo unusually flexible if you like both subscription browsing and occasional credit purchases.
Best fit: frequent listeners who enjoy discovering within a subscription catalog and want a lower monthly entry price.
Hoopla: best library app when you hate waiting lists
Hoopla complements Libby rather than replacing it. Participating libraries provide access, and Hoopla’s Instant collection is designed around immediate borrowing without holds. A 2026 Hoopla library sheet lists more than 385,000 audiobooks within an Instant catalog of more than 2 million titles across formats. Some libraries also use Hoopla Flex, where newer ebooks and audiobooks can involve availability and holds.
Your real limit is set by the library. One system may allow a generous number of Instant borrows each month, while another may set a much smaller cap. That means a national feature list cannot tell you exactly how much Hoopla you personally receive.
Best fit: library users who prioritize instant access and want a second free catalog alongside Libby.
Chirp: best for cheap audiobooks without a subscription
Chirp is useful precisely because it refuses the monthly-credit model. There is no subscription or membership fee. Instead, Chirp runs rotating audiobook discounts, with current deal pages advertising offers starting at $1 and discounts of up to 95% on selected titles. Purchases are yours to keep, and you can stream them or download them in the Chirp app for offline listening.
The weakness is selection at the exact moment you want a specific book. Chirp is a deal hunter’s service, so the best savings come from being flexible about what you buy and when. It is currently available in the United States and Canada.
Best fit: occasional buyers, bargain hunters, and listeners who dislike recurring subscriptions.
Apple Books and Google Play Books: best built-in pay-as-you-go stores
Apple Books and Google Play Books are strong choices when the ideal subscription is no subscription at all. Apple lets users buy audiobooks individually in the Books app, download purchases, change playback speed, and use a sleep timer. Google Play Books also sells audiobooks individually and syncs listening position across supported devices; Google says some titles can be exported, depending on publisher settings.
Neither store needs to beat Audible on membership perks to be useful. Their advantage is frictionless one-off buying inside ecosystems many people already use. If you finish only a few audiobooks a year, comparing the per-title price can be more economical than paying twelve months of subscription fees.
Best fit: occasional listeners who want straightforward purchases tied to an Apple or Google account.
How should you choose the best audiobook app for your habits?
A simple decision rule works better than obsessing over catalog size. Match the payment unit to the way you actually listen.
| Listening habit | Best match | Why it works | Watch for |
| You listen to one long premium book each month | Audible Premium or Libro.fm | One credit can cover a long eligible title without counting hours | Compare ownership terms and exclusives |
| You want to spend nothing | Libby first, Hoopla second | Both use library access rather than a paid consumer subscription | Catalogs and borrow limits depend on your library |
| You already pay for Spotify Premium | Spotify | The included 15 hours can add value without another base subscription | Long books can exceed the monthly allowance |
| You read ebooks and listen to audiobooks | Everand or Kobo Plus Read & Listen | One plan covers both formats | Most access ends when the subscription ends |
| You buy only when a deal is good | Chirp | No monthly fee and purchases are kept | The best discounts rotate |
| You listen only a few times a year | Apple Books or Google Play Books | Pay only for the title you want | Per-title prices can vary widely |
Is an hours-based plan or a credit-based plan better?
Credit plans are usually better for listeners who choose long audiobooks because one eligible book costs one credit regardless of runtime. Hours plans are better for casual listeners who sample shorter books or already receive the allowance inside another service. If your typical audiobook is 25 hours, calculate cost per completed title, not cost per month.
Should you keep more than one audiobook app?
Yes, because the models complement each other. A practical low-cost stack is Libby plus Hoopla for free borrowing, then one paid option for titles that are unavailable or have long waits. Heavy listeners can pair a credit service such as Audible or Libro.fm with Chirp for discounted extras instead of buying additional full-price credits every month.
What should you check before subscribing?
- Search for three specific books you genuinely want, including one recent release and one long title.
- Check whether credits, unlocks, or listening hours expire and what happens after cancellation.
- Confirm that offline downloads work on the device you use most.
- Check country availability and regional catalog restrictions before comparing headline prices.
- Estimate your real monthly listening hours so you do not pay for unused access.
Verification sources for current plan details
The plan and catalog facts in this guide were checked against official service pages available on August 21, 2026. Key references include:
Audible plans | Audible plan help | Spotify Premium audiobook rules | Spotify U.S. audiobooks
Libro.fm membership rules | Libby borrowing help | Everand plans | Kobo Plus U.S. plans
Chirp how it works | Apple Books audiobook help | Google Play audiobook help | Hoopla 2026 library sheet
Hoopla patron access and monthly borrow limits are determined by each participating library.
Conclusion: choose the payment model before the app
The best audiobook app is the one whose limits match your listening behavior. Audible is the strongest paid default for a listener who wants a permanent credit purchase each month, while Libro.fm offers a compelling ownership-focused alternative with DRM-free files and indie bookstore support. Libby and Hoopla should be on almost every library user’s phone because free borrowing changes the economics completely. Spotify works best as an add-on to a subscription you already value, while Everand and Kobo Plus reward readers who consume across formats or browse widely. Chirp, Apple Books, and Google Play Books make the most sense when you would rather buy selectively than maintain another recurring bill.
Before paying, search for the next three audiobooks on your actual reading list. That five-minute test will tell you more than a catalog-size headline ever will.
FAQs about the best audiobook apps
What is the best audiobook app if I do not want a subscription?
Chirp is a strong option for discounted purchases without a monthly fee, while Apple Books and Google Play Books are straightforward pay-per-title stores. The best choice depends on whether you prefer deal hunting or buying a specific title immediately.
Which audiobook app lets me keep books after I cancel?
Audible Premium credit purchases, Libro.fm purchases, Chirp purchases, and standard purchases from Apple Books or Google Play Books remain in your library after cancellation or do not require a subscription in the first place. Subscription-catalog access from services such as Kobo Plus ends when the subscription ends.
Is Libby better than Audible?
Libby is better for free borrowing if your library has the titles you want. Audible is better when you need a specific premium title immediately and want a purchase model that does not depend on local library licensing or wait lists.
Is Spotify enough for audiobooks?
It can be for casual listeners. Eligible Spotify Premium plans include 15 audiobook hours per month in the U.S., but long books can exceed that allowance, and unused included hours expire at the monthly reset.
What is the cheapest audiobook app for heavy listeners?
If the titles you want are in its catalog, Kobo Plus Listen is a low-cost subscription option at $7.99 per month in the U.S. Library apps can be cheaper still because Libby and Hoopla are free through participating libraries.
Can I listen to audiobooks offline on these apps?
Most major options in this guide support offline listening in their mobile apps, including Audible, Libby, Libro.fm, Everand, Kobo, Chirp, Apple Books, and Google Play Books. Exact download rules can vary by platform and title, so confirm device support before a trip or long period without internet access.
The best Wireframing tools in 2026 are not the ones with the longest feature lists: Figma is strongest when a rough layout must grow into production design, Balsamiq is better when deliberate low fidelity keeps discussion focused, and AI-first products such as Uizard and Visily are useful when speed matters more than deep interaction logic. The expensive mistake is choosing a tool for the first ten minutes of sketching instead of the next ten weeks of product work.
I reviewed ten high-visibility guides for this query, then checked vendor pricing, product changes, and recent design-industry research. Most ranking pages do a decent job naming popular apps. The gap is decision context. A founder, UX designer, product manager, and enterprise design team can all search the same keyword while needing different levels of fidelity, collaboration, governance, and developer handoff.
I treat a wireframe as a decision artifact, not a mini mockup. It should answer questions about hierarchy, navigation, content priority, task flow, and system behavior before visual polish makes changes expensive. When navigation is the problem, information scent matters more than button color. The same principle appears in Aperplexity’s guide to shortcut navigation: labels and task priority should reduce search cost rather than create another layer of confusion.
The shortlist below compares ten current products, but I do not force a universal winner. I rank them by the uncertainty they can resolve, the distance between wireframe and handoff, and the cost of switching tools later. That creates a more useful answer than another feature-count contest.
What should a wireframing tool actually help you decide?
A wireframing tool should make structure cheap to change. At minimum, it needs reusable interface elements, fast rearrangement, comments or sharing, and enough prototyping to expose a broken flow before engineering starts. The right fidelity depends on the question. If I am debating information architecture, polished typography is noise. If I am testing permissions, validation, or branching states, a static sketch is too weak.
Visual polish can create commitment before the structure is stable. I call that fidelity debt: time spent making an unresolved idea look final, plus the cost of persuading people to discard it later.
How I ranked these wireframing tools
I weighted seven factors: speed to first useful screen, control over fidelity, collaboration, interaction depth, AI assistance, developer handoff, and current paid-seat cost. I also checked platform constraints and product lifecycle risk. I did not award extra points simply because a product can do more.
The key test is reversibility. An early artifact should be cheap to change and still have a credible path forward. A fast draft that must be rebuilt before testing or handoff may not be fast overall.
Match the tool to the uncertainty, not the job title
This is the framework I found most useful after comparing the SERP. Start by naming the uncertainty that could still invalidate the design. Then choose the lowest fidelity that can answer it. The result is often different from choosing by team size or by a generic “best overall” score.
This matrix turns the decision into a testable design question rather than a popularity ranking.
| Uncertainty | Useful fidelity | Strong fit | Main risk |
| Navigation or content hierarchy | Low fidelity | Balsamiq, Whimsical | Premature visual detail |
| Workshop alignment | Shared low fidelity | Miro, Whimsical | A board that becomes an unowned archive |
| Fast concept exploration | AI-assisted low to mid | Uizard, Visily | Accepting generated conventions without review |
| Design system continuity | Mid to high | Figma, Sketch | Polishing before core flow is stable |
| Complex states or business rules | Interactive logic | Axure RP | Overbuilding simple flows |
| Production component behavior | Code-backed prototype | UXPin, Penpot | Tooling complexity before the system is mature |
Best wireframing options at a glance
Prices below are public starting rates checked on September 11, 2026. They are snapshots, not permanent quotes.
| Tool | Best for | Free entry | Starting paid price | Main trade-off |
| Figma | Wireframe to production design | Free | From $16/full seat/mo annually | Easy to polish too early |
| Balsamiq | Deliberate low fidelity | Trial | From $16/editor/mo annually | Limited visual and interaction depth |
| Whimsical | Wireframes plus flows/docs | Free | From $10/editor/mo annually | Not a full production UI tool |
| Miro | Discovery workshops | Free | From $8/member/mo annually | General canvas can become messy |
| Uizard | Prompt-to-screen speed | Free | From $12/mo annually | AI output needs strong review |
| Visily | Non-designers and AI drafts | Free | From $11/editor/mo annually | Less depth for complex systems |
| UXPin | Code-backed design systems | Free/trial varies | From $29/seat/mo annually | Higher cost and learning curve |
| Axure RP | Logic-heavy prototypes | Trial | From $29/user/mo | Overkill for simple layout questions |
| Penpot | Open-source and self-hosting | Free | From $7/user/mo cloud | Smaller ecosystem than Figma |
| Sketch | Mac-native product design | Trial | From $12/editor/mo annually | macOS editor constraint |
Figma: best when the wireframe must become the final design
I would choose Figma when continuity matters more than enforced simplicity. The Professional Full seat is $16 per month on annual billing, and one file can move from gray-box structure to components, prototypes, and handoff. The risk is premature polish: an uncertain flow can look settled before it earns that confidence.
Balsamiq: best for deliberately low-fidelity alignment
Balsamiq is strongest when roughness is a feature. Its sketch-like components help keep reviews on hierarchy and flow, and current Starter pricing is $16 per editor per month billed annually. Lifecycle matters here: Balsamiq’s official transition timeline says Desktop sales end December 31, 2026, with support continuing through December 31, 2027. New projects should therefore favor its cloud product rather than a fresh Desktop dependency.
Whimsical: best for product teams mixing flows and screens
Whimsical works well when flows, diagrams, docs, and wireframes need to stay close together. Pro starts at $10 per editor per month billed annually. It bridges workshop thinking and structured screens, but its ceiling appears when the work needs detailed production design or advanced interaction logic.
Miro: best for collaborative discovery workshops
Miro fits when the wireframe is one artifact inside a broader discovery session. Starter is $8 per member per month on annual billing, and one board can hold research, journey maps, votes, notes, and rough UI. Governance still matters because an infinite canvas can become a storehouse of stale alternatives.
Uizard: best for turning prompts into fast first drafts
Uizard is useful when a founder, marketer, or product manager needs screens before a designer is available. Pro is $12 per month billed annually. I would use the generated screen as a hypothesis, not a specification. Generation compresses drawing time, but it does not validate task priority, edge cases, accessibility, or product fit.
Visily: best AI-assisted option for non-designers
Visily combines prompt generation, screenshot conversion, editable UI, and Figma import/export. Pro starts at $11 per editor per month billed annually. It suits cross-functional teams that want visual output without a steep learning curve. The trade-off is generated plausibility: each screen still needs a review tied to the assumption it is supposed to test.
UXPin: best for code-backed design-system prototypes
UXPin is strongest when the team already has a design system and wants prototypes closer to production behavior. Core starts at $29 per seat per month billed annually, making it materially more expensive than most list-first wireframing choices. The premium makes sense only when real components, state behavior, and handoff accuracy reduce downstream rebuilds.
Axure RP: best for complex states and business rules
Axure RP remains the specialist for variables, conditional logic, repeaters, and specification-heavy interaction. Pro is listed at $29 per user per month. I would reach for it when the risk sits in the behavior rather than the layout, such as enterprise approvals, permissions, calculators, or multi-step forms. For a basic landing-page wireframe, that complexity buys little useful evidence.
Penpot: best open-source and self-hostable option
Penpot is the strongest choice here for open source, self-hosting, and a standards-oriented path between design and code. Cloud Unlimited starts at $7 per user per month, while Professional self-hosting is free. Teams leaving Figma should still audit plugins, libraries, integrations, and migration effort before treating license savings as total savings.
Sketch: best for Mac-native interface design
Sketch still makes sense for Mac-centered teams that value a native editor and a mature design workflow. Standard pricing is $12 per editor per month billed annually. Its wireframes can mature into polished product UI without a tool change, but the editor remains tied to macOS. For mixed-device organizations, that platform boundary may matter more than the monthly price.
What does a five-person team actually pay?
Sticker price is easier to compare in one unit. The table multiplies the public starting rate by five editors and 12 months. It is a September 11, 2026 planning snapshot, not a quote; taxes, enterprise terms, AI overages, and billing choices can change the total.
| Plan | Rate used | Five-seat annualized cost |
| Penpot Unlimited | $7 | ~$420 |
| Miro Starter | $8 | ~$480 |
| Whimsical Pro | $10 | ~$600 |
| Visily Pro | $11 | ~$660 |
| Sketch Standard | $12 | ~$720 |
| Uizard Pro | $12 | ~$720 |
| Figma Professional Full | $16 | ~$960 |
| Balsamiq Starter | $16 | ~$960 |
| UXPin Core | $29 | ~$1,740 |
The calculation is rate x five paid editors x 12 months. It does not monetize migration time, training, or AI overages.
What are the biggest risks and trade-offs?
The first risk is fidelity debt. A polished frame can attract feedback on finish before hierarchy or task flow is settled. My workaround is simple: write the decision question above the canvas and refuse detail that cannot help answer it.
The second risk is AI anchoring. In Figma’s 2025 survey of 2,500 users, 78% said AI significantly enhanced work efficiency, but only 32% said they could rely on AI output. The same report found successful AI-product teams were more likely to explore multiple design or technical approaches, 60% versus 39% among unsuccessful teams. I read that as a strong argument for generating alternatives, not merely generating faster.
The third risk is migration cost. Files, components, comments, prototypes, permissions, and team habits all have switching costs that a monthly price table misses. Before changing platforms, I use the same assumption-testing discipline described in Aperplexity’s critical-thinking exercises: state the expected benefit, list evidence, and name the condition that would make the switch a bad decision.
How should you choose the right tool?
For a founder-led MVP, I would start with the product uncertainty, not the design brand. If the main question is scope, a low-fidelity tool plus a clear feature boundary is often enough; Aperplexity’s Startup Booted guide makes a related point about keeping founder decisions tied to practical deliverables and constraints.
For a product team, I would optimize for handoff distance: how many times the artifact must be recreated before it reaches the person who builds it. Figma, Sketch, UXPin, and Penpot can shorten that distance. Balsamiq, Miro, and Whimsical can still be better when the early decision is cheap enough that preserving the artifact is less important than preserving clarity.
For AI-generated drafts, I use one rule: generation may propose the first arrangement, but a human must own the final hierarchy, states, accessibility, and evidence. That is consistent with Aperplexity’s analysis of AI detector limits, where automated output is treated as a signal to inspect rather than a verdict to accept.
The Future of Wireframing Tools in 2027
I expect wireframing in 2027 to become less about drawing rectangles and more about controlling the transition from intent to testable behavior. AI generation is already moving from blank-canvas assistance toward editable prototypes, code-aware components, and agentic workflows. The important constraint will be review quality, not raw generation speed.
That direction has measurable momentum. Figma reported in its August 2026 results that more than 80% of paid customers above $10,000 in annual recurring revenue were consuming AI credits weekly as of June 30, 2026. Dylan Field also argued at Config 2025 that “design is a differentiator that will make great companies and products stand out” (Figma, 2025b). I therefore expect the winning products to combine faster generation with stronger systems, governance, and handoff rather than eliminate design judgment.
Key Takeaways
- Choose fidelity according to the uncertainty that can still invalidate the product decision.
- Use low fidelity to keep navigation and hierarchy reversible; use richer prototypes only when behavior needs evidence.
- AI is valuable for option generation, but the efficiency gain is not the same as trustworthy output.
- Calculate seat cost and migration cost together because the cheaper subscription can still create a more expensive workflow.
- Check lifecycle risk before adopting a tool, especially when a desktop product or legacy workflow is being retired.
- Minimize handoff distance when a wireframe is expected to mature into production design or code-backed components.
Conclusion
The best choice is the one that makes the next important decision cheaper and clearer. I would use Balsamiq when roughness protects the conversation, Figma when continuity to production matters, Miro or Whimsical when discovery is collaborative, Uizard or Visily when fast visual generation unlocks discussion, and Axure or UXPin when behavior is the real uncertainty. Penpot deserves special attention when open source or self-hosting is a requirement, while Sketch remains practical for Mac-native teams.
What I would not do is pick from a feature checklist alone. A low monthly price can hide rebuild work, and an impressive AI demo can hide weak reasoning. The durable approach is to name the uncertainty, choose the lowest useful fidelity, compare the cost of the whole path, and set a clear review threshold before the artifact becomes expensive to change. That keeps wireframing what it should be: a fast way to learn before implementation locks the answer in.
Frequently Asked Questions
What are the best free wireframing tools?
Figma, Miro, Whimsical, Visily, Uizard, and Penpot all offer some form of free entry, although limits differ by files, boards, projects, AI credits, or collaboration. Penpot is especially notable because its Professional self-hosted edition is free. Always check the current plan page before standardizing a team workflow.
Which wireframing tool is best for beginners?
Balsamiq is one of the easiest choices when a beginner needs to communicate layout without learning a full interface-design system. Whimsical is also approachable for teams that need flows and diagrams. AI-first tools can create a faster first draft, but beginners still need to review hierarchy and task logic.
Is Figma good for wireframing?
Yes. Figma is particularly strong when the wireframe is expected to mature into high-fidelity UI, components, prototypes, and developer handoff in the same workspace. Its main drawback is that access to polished design features can encourage teams to increase fidelity before the product structure is stable.
Should I use low-fidelity or high-fidelity wireframes?
Use low fidelity when the question is structure, navigation, scope, or content priority. Increase fidelity when the question depends on interaction, visual hierarchy, component behavior, or usability details. The right level is the cheapest one that can produce credible evidence for the decision you need to make.
Can AI create usable wireframes?
Yes, AI can generate useful first drafts from prompts, screenshots, or sketches, especially in Uizard, Visily, and increasingly broader design platforms. I would treat those drafts as alternatives to evaluate. AI can accelerate arrangement, but it does not know your product constraints, research evidence, accessibility obligations, or edge cases unless you supply and verify them.
What is the difference between wireframing and prototyping?
A wireframe primarily represents structure, hierarchy, and flow. A prototype adds enough interaction to simulate behavior and support testing. The boundary can blur because modern tools support both, but the decision rule is simple: add interaction only when a static frame cannot answer the question under review.
Methodology
I researched this article through September 11, 2026. I reviewed ten high-visibility ranking pages for the focus query and close variants, then validated current prices and lifecycle details against vendor pages. For market context, I used Figma’s 2025 AI report and August 2026 financial results. Internal links were selected only from live aperplexity.com pages where the surrounding idea was directly relevant.
The main SERP gap I targeted was not another longer list. Several leading pages already organize products by use case or fidelity. I therefore added an uncertainty-to-fidelity framework, five-editor annualized cost math, fidelity debt, AI anchoring, and lifecycle risk. Prices are snapshots, and search rankings vary by location, personalization, and date. I did not conduct fresh hands-on product testing, so first-person language describes research, comparison, and editorial analysis rather than fabricated usage.
AI assistance was used to research, organize, and draft this article. A human editor must review the final text before publication, verify named claims and APA references against the original sources, click every internal and outbound link, and confirm that all first-person statements accurately describe the author’s real editorial process.
References
Figma, Inc. (2025a, April 24). Figma’s 2025 AI report: Perspectives from designers and developers.
Figma, Inc. (2026, August 5). Figma announces second quarter 2026 financial results.
Balsamiq Studios. (2025, June 6). The future of Balsamiq for Desktop.
BOMBitUP is an Android app associated with bulk SMS, repeated calls, and email bursts, but the most important fact is not how many messages it can send. It is that the same mechanism marketed as a prank can become spam, harassment, or a way to bury legitimate security alerts when the recipient never agreed to it. I reviewed the project’s current public documentation, its release history, ten high-visibility pages ranking for the keyword, Android security guidance, and telecom reporting guidance before writing this guide.
If you searched for this tool, you are likely trying to answer several questions at once: what the app is, whether a download is genuine, whether it is safe, whether its “Protect Me” feature works, or how to stop an OTP flood. Most ranking pages answer the download question first. I think that order is backwards. Before anyone installs an APK or enters a phone number into a protection form, they should understand the source, data trade-off, and legal risks.
The project’s own materials describe the software as an Android application created by RomReviewer, with SMS, call, and email modes connected to changing online integrations. The GitHub release history shows active versioning in 2026, while mirrors display conflicting version numbers and large download claims that I could not independently verify. That inconsistency changes how a reader should judge “official” pages.
My aim here is defensive and verification-focused. I did not install the app, send test traffic, or reproduce bombing behavior. I checked what can be verified from public sources and built a practical response for people deciding whether to trust the software or already receiving unwanted OTPs and calls.
What Does the App Actually Do?
It is a third-party Android utility that automates requests through online service integrations. The project documents SMS, call, and email modes. Those integrations can change, fail, or be blocked, so claims that a particular carrier, country, speed, or message count is guaranteed deserve caution (RomReviewer, 2026a).
A typical OTP flood can repeatedly trigger legitimate services that normally send verification codes, alerts, or callbacks. The recipient may then see messages from many unrelated brands. I am intentionally not reproducing operational steps because those details can make harassment easier.
For readers trying to understand authentication rather than prank tools, Aperplexity’s NCEdCloud MFA guide shows a legitimate use of one-time codes inside an identity workflow. That contrast matters: an OTP should confirm a real account action, not become background noise.
The project is also not a native iPhone app. An APK is an Android package. Pages claiming universal browser access are separate web implementations or mirrors, not proof of an official iOS release.
Why Are BOMBitUP Search Results So Confusing?
The search landscape mixes a project website, GitHub, APK distributors, review sites, and multiple domains calling themselves official. I found pages showing versions across the 4.x and 5.x series, plus mirror claims of 10 million, 63 million, 64 million, or 71 million downloads. I could not verify those totals.
The GitHub release history is more useful for chronology. Current search data lists version 5.0.1 in August 2026, while older cached pages and the repository README can still show older versions (RomReviewer, 2026b). A search snippet, mirror badge, or stale README should not be treated as a single source of truth.
I use this source hierarchy when software branding is fragmented.
Source-verification hierarchy for fragmented software branding.
| Source type | What it can establish | Main weakness | My trust level |
| Versioned project release history | Release tags, dates, publisher account | Does not prove harmless behavior | Highest for version history |
| Project privacy/terms pages | Declared data handling and rules | Self-published claims | High for stated policy |
| Major APK distributor | File metadata and historical versions | May lag the publisher | Medium |
| Mirror claiming “official” status | Current landing-page claims | Identity and download claims may be unverified | Low until verified |
| Random review/download page | Common questions and search intent | Often repeats secondary claims | Low for verification |
Aperplexity’s ChromiumFX guide applies the same source-first method to software version history and package status rather than trusting the first download page.
Is the APK Safe to Install or Use?
I would not give a blanket “safe” verdict. Technical file safety and behavioral safety are different questions. A clean APK could still enable abusive use, while a mirror could distribute a modified APK with risks not present in the publisher’s release.
Google says apps downloaded from unknown sources can put a device and personal information at risk. Play Protect checks apps from outside the Play Store and may warn, block, disable, or remove harmful software (Google, 2026a).
I would keep Google Play Protect guidance enabled and avoid weakening device security just because a download page asks me to.
What Does the Protection List Really Do?
The protection feature deserves more scrutiny than most ranking pages give it. The current project privacy policy says it asks for a first name and mobile number, and that a version 5.0.1 protection entry expires after two weeks (RomReviewer, 2026c). Project guidance also says the protection list applies only to its own ecosystem, not unrelated bombing tools.
That creates a trade-off. Submitting your number may reduce requests from that ecosystem, but you are also giving the service your number so it can maintain the block. I would only submit a number I control and would not assume the entry creates carrier-level protection.
Several ranking pages describe protection as instant, permanent, or universal. The project’s current policy is narrower, and that distinction matters more than a promotional feature list.
What Should You Do If Your Number Is Being Bombed?
If dozens of OTPs or calls arrive within minutes, focus on containment and account security rather than retaliation. A flood can be a prank, but it can also make a genuine fraud alert or password-reset message easier to miss.
I would use this order:
- Do not click links or reply to unfamiliar messages. Open important services from official apps or saved bookmarks.
- Check high-value accounts directly for sign-in alerts, password resets, or transactions you did not initiate.
- Preserve a few representative screenshots, sender names or headers, timestamps, and call-log entries.
- Use built-in spam controls and report suspicious messages through your messaging app.
- Contact your carrier if the flood persists and ask about spam filtering and abuse reporting.
- Treat the project protection list only as a limited extra measure, not a universal block.
- Escalate threats, stalking, extortion, or signs of account compromise to the appropriate local authority.
When OTP noise overlaps with suspicious sign-ins, I treat the messages as security evidence, not merely clutter. Aperplexity’s defensive guide to exposed logs and credentials applies the same principle: an automated signal should trigger verification, not unauthorized counter-action.
Country Reporting Options for OTP and Spam Abuse
Reporting systems differ, and a carrier may classify a bombing incident differently from ordinary commercial spam. This table gives a starting point, not legal advice.
Country-level reporting starting points for OTP and spam abuse.
| Country | First route | Official guidance | Note |
| India | Mobile provider and TRAI | 1909 and approved DND channels | Keep sender/header, date, time, and message details |
| United Kingdom | Mobile provider and 7726 | Ofcom scam-message guidance | Do not reply to unknown senders |
| United States | Mobile provider and FCC/FTC | Unwanted call/text complaint channels | Use official account channels, not message links |
| Pakistan | Mobile provider and relevant cybercrime authority | FIA cybercrime guidance | Repeated unwanted contact may raise harassment concerns |
For UK readers, Ofcom’s scam-call and message guidance recommends not engaging with suspicious messages and using 7726 for SMS reporting. TRAI’s current spam-reporting guidance says Indian consumers can report spam through 1909 or approved DND channels (TRAI, 2026).
Is BOMBitUP Legal?
There is no single global law for the app. Legality depends on consent, purpose, volume, impact, and jurisdiction. I would avoid claims that the app itself is automatically legal or illegal everywhere.
The project’s own documentation makes prior consent central and says not to harass, threaten, disrupt services, or contact strangers. A disclaimer does not turn unwanted traffic into consent.
Telecom, privacy, anti-spam, harassment, and computer-misuse rules can all matter. The UK regulates electronic marketing under PECR (Information Commissioner’s Office, 2026). India provides formal UCC complaint mechanisms. The FCC regulates illegal robocalls and robotexts in the United States. Pakistan’s FIA guidance addresses repeated unwanted electronic contact in cyber-harassment contexts.
The practical rule is clearer than a legal slogan: if the recipient did not clearly agree, do not send automated floods.
How Does Bombing-Style Messaging Compare With Legitimate Bulk Messaging?
Bulk communication is not inherently abusive. Businesses, schools, banks, and emergency systems send messages at scale. The difference is authorization, identity, rate limits, and accountability.
How bombing-style traffic differs from legitimate bulk messaging and testing.
| Factor | Bombing-style use | Legitimate messaging/testing |
| Recipient consent | Often absent in abuse | Explicit consent or controlled test |
| Sender identity | May be fragmented across services | Identifiable sender |
| Volume | Designed to create bursts | Rate-limited to need |
| Purpose | Prank, disruption, or testing | Alerts, transactions, support, agreed tests |
| Protection | Project-specific | Provider, carrier, campaign, or account controls |
| Audit trail | Fragmented | Central logs and policies |
Authentication is also moving away from SMS in some enterprise systems. Microsoft began making passkeys the default Entra ID experience on September 1, 2026 and plans to retire Microsoft-provided SMS and voice authentication on February 1, 2027. Nadim Abdo wrote that passkeys “work better for users and worse for cyberattackers” (Abdo, 2026).
Aperplexity’s Entra Admin Center guide covers that migration. The connection is straightforward: when a channel can be phished, SIM-swapped, or flooded with noise, stronger credentials become more attractive.
The Future of BOMBitUP in 2027
I expect three pressures to shape this topic in 2027.
First, Android is tightening accountability around app distribution. Google’s 2026 developer-verification program expands publisher checks in selected markets, pushing the ecosystem toward stronger identity (Google, 2026b).
Second, authentication providers are reducing dependence on SMS and voice for high-value sign-ins. Microsoft’s February 1, 2027 Entra retirement is one concrete example of the move toward passkeys and other phishing-resistant methods.
Third, anti-abuse limits will keep changing how bombing tools function. The project itself says third-party integrations can change. More rate limits, bot detection, and carrier filtering are more plausible than a permanent promise that one mirror will always work.
Enforcement will remain uneven across countries, and mirror domains can change quickly. I therefore expect source verification, device security, and carrier reporting to stay more useful than claims that a particular site is permanently “working.”
Key Takeaways
- The project has a public Android release history, but mirrors often disagree on versions and “official” status.
- The project’s protection policy says it collects a first name and mobile number and that the block expires after two weeks.
- A technically clean APK is not the same as safe behavior. Non-consensual automated messaging can still become harassment.
- Play Protect matters because sideloaded apps sit outside the normal Play Store distribution path.
- An unexpected OTP flood should trigger a direct review of important accounts.
- Carrier and regulator reporting paths differ, but timestamps, sender headers, and call logs are useful evidence.
- The 2027 direction favors stronger app-source verification and phishing-resistant authentication.
Conclusion
I would not judge the app by a single “safe” or “dangerous” label. The more useful judgment separates four questions: who published the file, what the release record shows, what data a protection feature asks you to submit, and whether the intended use has the recipient’s clear consent.
The search results make that harder than it should be. Multiple domains use “official” language, mirror pages publish conflicting versions and large download totals, and many articles focus on installation before they explain the risks. The verifiable picture is narrower: the RomReviewer project has a public release history, the current policy describes a time-limited protection list, and Android warns that unknown-source apps deserve extra scrutiny.
If you are already receiving OTP spam, do not retaliate with another bomber. Check important accounts directly, preserve evidence, use device and carrier spam controls, and report persistent abuse. That protects the one thing a message flood tries to take away: your ability to distinguish a real security event from noise.
Frequently Asked Questions
What Is This App Used For?
The Android utility is associated with automated SMS, call, and email requests. Its current documentation frames these as consent-based testing or prank features. The same automation can become spam or harassment without consent.
Is the APK Safe for Android?
No universal verdict applies to every APK or mirror. Google warns that unknown-source apps can expose devices or personal data to risk. Verify the publisher and release source, keep Play Protect enabled, and review permissions.
What Is the Latest BOMBitUP Version?
Current GitHub search data shows version 5.0.1 in the project’s 2026 release history, but cached pages and mirrors can show older versions. Use the versioned release history for chronology rather than a mirror’s “latest” badge.
Does the Protection List Protect My Number Permanently?
The current project privacy policy says a protection entry includes a first name and mobile number and expires after two weeks. It applies to that ecosystem, not every unrelated bombing service.
Can OTP Bombing Hide a Real Hack?
It can create enough noise to make a genuine password-reset, sign-in, or fraud alert easier to miss. A flood does not prove compromise, but it is a reason to review important accounts directly.
Is This App Legal in India, Pakistan, the UK, or the US?
There is no single global status. Consent, purpose, impact, and local law matter. Telecom, privacy, anti-spam, harassment, and computer-misuse rules can apply differently.
Is There a Native iPhone App?
The project is distributed as an Android APK and does not describe a native iOS app. Browser-based pages are separate web tools or mirrors, not proof of an official iPhone application.
Methodology
I researched this article through September 9, 2026. I reviewed ten high-visibility results for the keyword, including the project website, GitHub, mirrors, APK distributors, and review pages. Exact search order can vary by country, personalization, and index freshness, so I treated the set as a current SERP sample.
For validation, I prioritized the RomReviewer release history and privacy policy, Google Android security guidance, Microsoft’s 2026 passkey announcement, TRAI, Ofcom, FCC, FTC, ICO, and FIA guidance. I verified four internal Aperplexity pages through current search results.
I did not install or operate the app, trigger messages, reverse-engineer its APIs, or test mirror APKs. I also could not independently verify the large download totals claimed by several mirrors. Legal outcomes vary by jurisdiction and facts, so this article is not legal advice.
AI assistance was used to support research organization and drafting. A human editor must verify named claims, references, link destinations, and final wording before publication.
References
Abdo, N. (2026, July 13). Microsoft Entra ID security updates: Passkeys are the default authentication method in Entra ID. Microsoft Security Blog.
Federal Communications Commission. (n.d.). Unwanted calls/texts: Phone. Consumer Inquiries and Complaints Center.
Federal Trade Commission. (2025, April). Is that unexpected text a scam? Consumer Advice.
Federal Investigation Agency. (2025). Cyber crimes: Risks, prevention and legal remedies. Government of Pakistan.
Google. (2026a). Use Google Play Protect to help keep your apps safe and your data private. Android Help.
Google. (2026b). Learn about Android developer verification. Android Help.
Information Commissioner’s Office. (2026, April 28). Guidance on direct marketing using electronic mail.
Ofcom. (2026, July 15; updated August 24, 2026). What to do about a scam call, text or message.
RomReviewer. (2026a). BOMBitUP official project website and responsible-use documentation.
RomReviewer. (2026b). BOMBitUP releases. GitHub.
RomReviewer. (2026c, August 23). Privacy policy. BOMBitUP.
Telecom Regulatory Authority of India. (2026, August 25). Complain or report against unsolicited commercial communications.
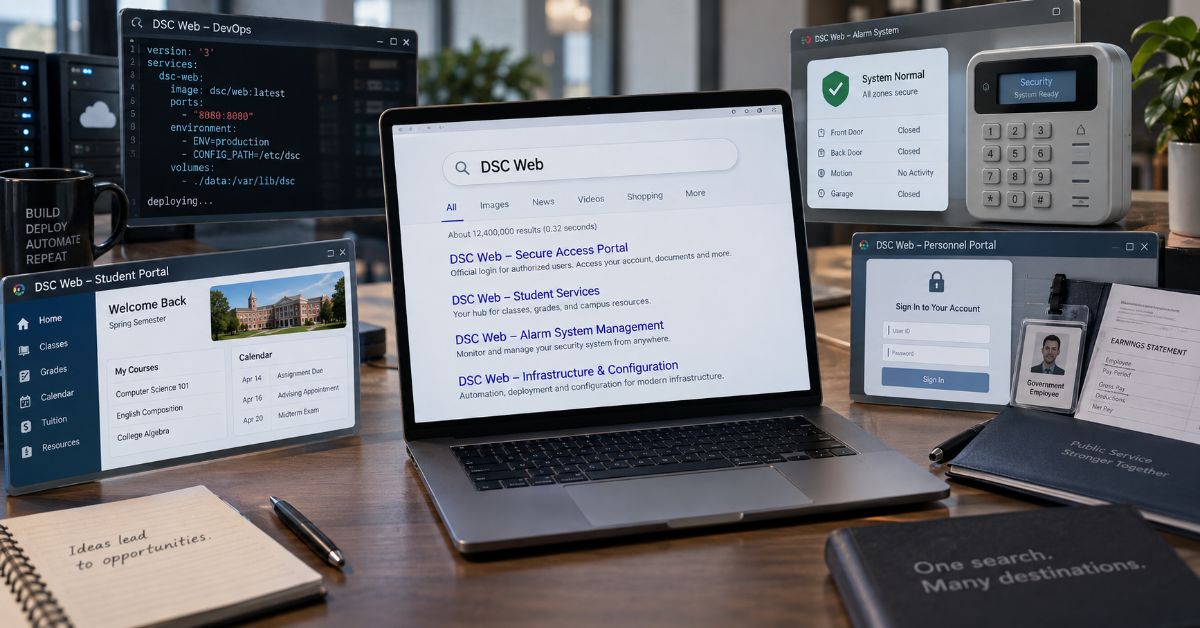
If you searched for DSC Web, the most useful answer is that there is no single DSC website. The phrase currently points to several unrelated destinations, including Microsoft Desired State Configuration, a live DSC alarm-communicator testing site, the Defence Security Corps portal in India, Daytona State College services, and other organizations that share the initials. I reviewed current search results on September 9, 2026, and that ambiguity is exactly why a one-definition article can send a reader to the wrong system.
I treat this query as an intent problem before I treat it as a definition problem. If you are a Windows or DevOps administrator, you probably need Microsoft DSC documentation, and the biggest trap is version drift: modern Microsoft DSC 3 is a standalone cross-platform command-line platform, while older ranking pages still describe the classic PowerShell pull server and report service. If you work with DSC security hardware, the browser destination has a completely different job. The public test site is designed for IP communicator testing, not as a general homeowner dashboard. If you are a Defence Security Corps user, the official portal is for service records, pay information, forms, grievances, and role-specific logins.
My goal here is to help you identify the right entity in under a minute, then give you enough context to avoid an outdated Microsoft workflow, an unrelated company, or a risky lookalike login. I also separate official portals from tools that merely use DSC in their names. Once you know which branch matches your task, the rest of the article gives you the correct workflow, current 2026 context, and a practical verification checklist.
What Does This DSC Search Actually Mean?
The phrase behaves like a crossroads. The fastest answer comes from the task around the initials, not from the initials alone. I use this map to route the search before opening a login or technical guide.
| Your Clue | Likely Entity | Correct Context |
| Configure systems declaratively | Microsoft DSC 3 | Current dsc CLI and configuration documents |
| LCM, MOF, pull/report server | Classic PowerShell DSC | Legacy Windows architecture |
| Export Microsoft 365 tenant settings | Microsoft365DSC | Browser-assisted export workflow |
| Test an alarm communicator | Digital Security Controls | Installer testing environment |
| Pay slip, Form 16, veteran login | Defence Security Corps | Official personnel portal |
| Classes, tuition, grades, Falcon | Daytona State College | Student portal |
| Convention or club events | Dallas Safari Club / Detroit Sportsmen’s Congress | Organization websites |
If You Mean Microsoft DSC, Start With the Version
For new infrastructure work, I would start with Microsoft’s current Desired State Configuration overview. Microsoft describes DSC as a declarative platform whose standalone dsc command runs on Windows, Linux, and macOS. It separates the desired state from the logic used by resources to reach that state (Microsoft, 2025).
Current configuration documents support operations such as dsc config get, test, and set. The platform can use resources implemented in different languages and is designed to integrate with higher-order orchestration tools. That makes the modern mental model an engine and resource system, not a mandatory browser console.
Release context also matters. GitHub marks v3.2.3, released July 16, 2026, as the latest stable build, while v3.3.0-rc.2 was released August 24 as a pre-release. Microsoft senior product manager Jason Helmick said v3.2 was shaped by real-world use, partner feedback, and community contributions. The release added built-in Windows resources, experimental Bicep integration over gRPC, version constraints, richer expressions, and adapter improvements (Helmick, 2026; PowerShell, 2026).
I also keep configuration separate from identity administration. Aperplexity’s Entra Admin Center guide covers the Microsoft browser control plane for users, authentication, roles, and Conditional Access. A sign-in or identity-policy failure is a different layer from a DSC resource failure.
Why do classic pull-server pages still rank?
Windows PowerShell DSC 1.1 used a Local Configuration Manager and could retrieve configurations from an IIS-based pull server. Microsoft’s report-server page still documents that model, but it also says the Windows Feature DSC-Service pull server has no planned new features or capabilities (Microsoft, 2023). The document can therefore be authentic and still be the wrong blueprint for a new DSC 3 design.
Where does the Microsoft365DSC browser UI fit?
Microsoft365DSC documents a browser interface launched with Export-M365DSCConfiguration -LaunchWebUI to help select Microsoft 365 components and generate an export command. I treat that as separate Microsoft 365 configuration tooling, not as the core DSC 3 interface (Microsoft365DSC, n.d.).
If a Windows node behaves unpredictably, I also separate drift from operating-system corruption. The DISM RestoreHealth guide is a practical boundary check before rewriting configuration to solve a damaged servicing layer.
| Technology | Execution Model | Best Fit |
| Microsoft DSC 3 | Standalone dsc CLI | Current cross-platform configuration as code |
| PowerShell DSC 1.1 | LCM + MOF + pull/report services | Legacy Windows deployments |
| Microsoft365DSC | PowerShell module + optional browser generator | Microsoft 365 tenant capture and drift workflows |
If You Mean DSC Alarm Systems
Digital Security Controls uses DSC for electronic security. Its official manufacturer site provides product, technical-library, owner, installer, software, and professional-login paths.
Its IP Communicator Live Interactive Testing Site is narrower. The page identifies itself as a 24/7 test environment for DSC IP communicators and says its live table refreshes every 30 seconds (Digital Security Controls, 2026). I reviewed the public page but do not reproduce live account, network, or event values because they add risk without helping the reader.
A test receiver is not a general homeowner dashboard. Owners should start from their installed product, monitoring provider, supported app, or installer. Installers testing communicator delivery should use the test environment and model-specific guides.
For accounts that expose devices or professional services, I would also use the strongest supported login protection. Aperplexity’s 2FA guide explains factor strength and recovery without assuming that a familiar login page is safe by itself.
If You Mean the Defence Security Corps Portal
The official Defence Security Corps portal serves personnel and veterans in India. Current pages list pay slips, Form 16, grievances, posting information, and separate individual, unit, veteran, administrative, and directorate login paths (Defence Security Corps, 2026).
This is mainly navigational intent. Verify the government hostname and correct role before entering service credentials. The portal also states that unauthorized access or misuse of personnel information is prohibited.
I would then save a verified canonical bookmark. That matches the principle in Aperplexity’s Quick Links guide: stable destinations beat repeatedly trusting whichever login-looking result ranks first.
Other Common Meanings You Should Not Ignore
Daytona State College uses DSC as an institutional abbreviation. Its support material says Falcon Self-Service / MyDaytonaState handles registration, tuition, holds, grades, financial aid, graduation, and profile updates after acceptance (Daytona State College, 2026).
Dallas Safari Club uses the initials for a very different audience. Its official convention page lists the 2027 Convention and Sporting Expo for January 7-10, 2027, at the Georgia World Congress Center in Atlanta (Dallas Safari Club, 2026). Detroit Sportsmen’s Congress is another legitimate organization using the initials. Search clues such as Falcon, tuition, convention, exhibitor, or club events resolve these meanings quickly.
How Do You Verify the Right Page Before You Sign In?
- Name the task first: configuration, alarm testing, service records, college access, or event information.
- Check the organization and hostname before credentials or downloads.
- On Microsoft pages, check version labels and architecture terms. LCM, MOF, ReportServerWeb, and xDscWebService signal the older generation.
- Prefer a canonical landing page over a deep login result when sensitive records or administrative tools are involved.
- Do not republish operational identifiers from live status or test pages merely because they are publicly visible.
That final rule reflects the same distinction in Aperplexity’s defensive log-exposure guide: public discoverability and safe handling are not the same thing.
| Clue Words | Likely Destination | Verification |
| dsc config, YAML, resource | Microsoft DSC 3 | Check current docs and release |
| LCM, MOF, pull server | Classic PowerShell DSC | Check “Applies To” and version |
| T-Link, communicator, receiver | Digital Security Controls | Use installer/product context |
| Pay slip, Form 16, veteran | Defence Security Corps | Verify government hostname |
| Falcon, tuition, grades | Daytona State College | Use college portal |
What the Current Ranking Pages Commonly Miss
- The real problem is entity collision. Individually correct pages can collectively create a poor result because they answer different intents.
- Microsoft version drift is part of the search answer. Old pull-server documentation can be authoritative yet inappropriate for a new DSC 3 project.
- A browser page is not automatically an account dashboard. The alarm test receiver, Microsoft365DSC generator, and government personnel portal all use the web for different jobs.
The trade-off is that a broad intent guide cannot replace every product manual or deployment tutorial. Its value is earlier in the journey: get the reader onto the right branch, label legacy versus current architecture, and reduce unsafe or irrelevant clicks. Once the branch is known, specialist documentation should take over.
The Future of DSC Web in 2027
For Microsoft, the verified direction is continued development of the standalone v3 engine, not a return to the classic always-on pull-server model. DSC 3.2 reached general availability in April 2026, v3.2.3 became the latest stable patch in July, and v3.3 reached release-candidate status in August. I found no Microsoft announcement that the core product is becoming a hosted browser dashboard.
The more defensible 2027 expectation is deeper integration. Version 3.2 already added experimental Bicep orchestration over gRPC, more built-in Windows resources, version constraints, extensions, and adapter improvements. The wider search will remain ambiguous because the alarm, military, education, convention, and club meanings continue independently. A ranking page should therefore keep its intent map and official destinations current instead of betting on one definition.
Key Takeaways
- Identify the entity before choosing a result.
- For new Microsoft work, start with DSC 3 and check the latest stable release.
- Treat classic pull-server pages as generation-specific documentation, not the default modern architecture.
- Keep the alarm test environment, Microsoft365DSC generator, and personnel portals in their documented roles.
- Verify official hostnames before logins, downloads, or bookmarks.
- Refresh the guide as releases and portal paths change.
Conclusion
I would not define this search with one sentence and stop. Several valid answers coexist, and choosing the wrong one can mean wasted time, an outdated infrastructure design, or credentials entered into the wrong service.
For Microsoft administrators, the key correction is architectural. Current DSC 3 is a standalone, cross-platform configuration platform centered on the dsc command, resources, and configuration documents. Classic PowerShell pull-server and report-server material can still matter in systems that intentionally run that generation, but it should not silently become the blueprint for new work. Microsoft365DSC’s browser generator is another separate tool with a Microsoft 365 tenant-export purpose.
For everyone else, context wins. Alarm installers, Defence Security Corps personnel, Daytona State students, convention visitors, and club members each need a different destination. My rule is consistent: identify the entity, verify the official hostname and role, then bookmark the canonical page. That small sequence turns an ambiguous search into a much safer and faster path.
Frequently Asked Questions
What does this DSC search usually refer to?
It can refer to Microsoft Desired State Configuration, Digital Security Controls alarm tooling, the Defence Security Corps portal in India, Daytona State College services, Dallas Safari Club, Detroit Sportsmen’s Congress, or other organizations. Context words such as PowerShell, alarm, veteran, Falcon, or convention usually identify the intended entity.
Does Microsoft DSC have a browser dashboard?
The core Microsoft DSC 3 platform is centered on the standalone dsc command, resources, and configuration documents. Microsoft365DSC separately offers a browser-assisted export generator, while classic PowerShell DSC used web-hosted pull and report services. Those are distinct architectures and projects.
What is a DSC pull server?
In classic Windows PowerShell DSC, a pull server is a centralized service that nodes can use to retrieve configurations and resources. Microsoft still documents that older architecture, but its report-server page says the Windows Feature DSC-Service pull server has no planned new capabilities. Check the generation before deploying it.
Is the DSC alarm testing site a homeowner login?
No. The public page identifies itself as an IP communicator live testing environment. Homeowners should start with their specific product, monitoring provider, supported app, or installer. Installers can use the test environment according to the manufacturer’s application and installation guidance.
What is the Defence Security Corps portal used for?
The official Indian portal provides services for personnel and veterans, including pay slips, Form 16, grievances, posting information, and role-specific logins. Verify the official government hostname and the correct account role before entering credentials.
How do Daytona State students access online services?
Daytona State College directs students to MyDaytonaState and Falcon Self-Service for registration, tuition, holds, grades, financial aid, graduation, and profile tasks. Clues such as Falcon, classes, tuition, or student email point to the college meaning rather than Microsoft or alarm systems.
Methodology
I researched this article on September 9, 2026, after reviewing ten prominent current results and close variants. I used that benchmark to identify entity collision, Microsoft version drift, and missing decision support without copying competitor structure or wording.
For validation, I prioritized Microsoft Learn, PowerShell/DSC releases, the PowerShell Team, Digital Security Controls, Defence Security Corps, Daytona State College, Dallas Safari Club, and Microsoft365DSC. I also verified every Aperplexity internal link used in the body.
Rankings vary by location, personalization, device, and time. I did not deploy DSC, alter an alarm communicator, sign into personnel records, or access a private student account. First-person statements describe research and editorial analysis, not invented testing.
AI assistance was used to organize research and draft the article. A human editor must verify claims, APA references, links, portal paths, and first-person statements before publishing.
References
- Microsoft. (2025, June 9). Microsoft Desired State Configuration overview. Microsoft Learn.
- Helmick, J. (2026, April 29). Announcing Microsoft Desired State Configuration v3.2.0. PowerShell Team.
- PowerShell. (2026). DSC releases. GitHub.
- Microsoft. (2023, June 21). Using a DSC report server. Microsoft Learn.
- Microsoft365DSC. (n.d.). Taking a snapshot of existing tenant.
- Digital Security Controls. (2026). Official security site and IP communicator test site.
- Defence Security Corps. (2026). Official portal for serving personnel and veterans.
- Daytona State College. (2026, June 30). What is Falcon Self-Service/MyDaytonaState?
- Dallas Safari Club. (2026). 2027 Convention and Sporting Expo.
-

 Technology3 weeks ago
ThomsonKids.com: Website Guide, Topics & Trust Check
-

 General2 weeks ago
Voozon.com: What It Is and How the Platform Works
-

 Technology2 weeks ago
thesindi com Review: What TheSindi.com Really Offers
-

 Technology2 weeks ago
Cambro.tv: Status, Safety & Technical Guide
-

 Business3 weeks ago
5starsstocks.com Review: Features, Trust and Safety
-
 General3 weeks ago
My Reading Manga: What MyReadingManga Is, Safety, Legality and Better Alternatives
-
 Guide3 weeks ago
Thothub Safety Guide: What the Name Means, Link Risks and Legal Concerns
-
 Technology4 weeks ago
Iwara: What iwara.tv Is, How It Works and What to Know